Short answer: To enable RDP on Windows Server, open Server Manager. Select Local Server and click Disabled next to Remote Desktop. Allow remote connections and keep Network Level Authentication on. On Server Core or remote machines, we'd set the registry value to 0 and enable the Remote Desktop firewall rule group in PowerShell.
To enable RDP on Windows Server, you start in Server Manager. The whole thing takes about 45 seconds. We’d leave Network Level Authentication on, and the same clicks work on every current version from Server 2016 to Server 2025.
- Server Manager: Local Server, Remote Desktop, Allow remote connections.
- PowerShell or CMD: the registry value plus the “Remote Desktop” firewall group.
- Server Core: SConfig option 7, then the firewall line.
Windows opens the firewall rules for TCP 3389 by itself. Every fresh install ships with Remote Desktop turned off, so this is the first real task on any machine.
The same steps apply almost anywhere a server lives. Racks at a hosting provider, desktop PCs under someone’s desk pretending to be servers, forgotten Hyper-V guests.
The version barely matters. The process is the same on all four current versions.
This page covers each route, and then the parts around it.
- The GUI method
- PowerShell
- CMD
- Server Core
- The firewall, which trips everybody up at least once
- NLA and security
The security section is long. A typical case: ransomware gets in through an open 3389 port.
The whole weekend then goes on rebuilding the file server from tape backups. So we’re not cutting that part short.
| Point | Detail |
|---|---|
| Default state | Remote Desktop is off by default on every Windows Server edition. The registry switch is fDenyTSConnections (0 = on) |
| Server Core and PowerShell | The registry alone is not enough. Turn on the “Remote Desktop” firewall rule group too |
| Security | Keep Network Level Authentication on and never expose port 3389 directly to the internet. Use a VPN or a firewall scope limited to trusted IPs |
| Sessions | Without the RDS role you get 2 concurrent administrative sessions. More users need Remote Desktop Services and RDS CALs |
| Detail | Info |
|---|---|
| Default RDP status | Disabled on all editions |
| Default port | TCP 3389 (UDP 3389 is also used for transport when available) |
| Admin sessions without RDS | 2 concurrent |
| Registry value | HKLM\System\CurrentControlSet\Control\Terminal Server\fDenyTSConnections |
| Firewall rule group | Remote Desktop |
| Works on | Server 2025, 2022, 2019, 2016 (Standard, Datacenter, Essentials) |
Before you enable RDP on Windows Server
Three checks prevent most lockouts.
| Check | Why |
|---|---|
| A local or domain administrator account | The Remote Desktop toggle is greyed out for regular users |
| A second way to reach the machine | A firewall mistake can lock you out |
| Knowing if a Group Policy already controls Remote Desktop | A GPO overrides local settings |
The admin account comes first, obvious as it sounds. A typical case: a junior tech reports a greyed-out toggle.
They had signed in with a regular domain user. That was the whole problem.
The second way in matters more.
| Ways in that don’t depend on the firewall |
|---|
| iDRAC |
| iLO |
| IPMI |
| A hypervisor console |
| A cloud portal console |
Picture a broken firewall rule on a colocation server with no other access. Two lines fix it. The round trip? Possibly 400 km and eight hours.
Cloud VMs differ. Providers such as Azure or AWS give you console access in their web portal.
Many enable RDP during provisioning anyway. So this page is mainly for bare-metal machines and freshly installed VMs.
It’s also for that one server where Remote Desktop mysteriously turned itself off. That was probably a GPO.
The method depends on where you sit and how many machines are involved.
| Situation | Method that fits |
|---|---|
| One server with a desktop | Server Manager |
| Server Core at the console | SConfig, then the firewall line |
| A script or a remote shell | PowerShell |
| A slow first PowerShell start | CMD |
| A jump box that already runs WAC | Windows Admin Center |
| Dozens of servers in one OU | Group Policy |
| RDP off and no console at hand | WinRM, PsExec or Remote Registry |
How to enable RDP on Windows Server with Server Manager
Windows enables the matching firewall rules automatically. The status changes to Enabled after a refresh.
- Open Server Manager. It launches after sign-in on most installs; if not, press Start and type
ServerManager. - Click Local Server in the left pane.
- Find “Remote Desktop” in the properties. It says “Disabled”, so click it.
- System Properties opens on the Remote tab. Pick “Allow remote connections to this computer”.
- The checkbox underneath mentions Network Level Authentication. Leave it on.
- Click OK. A note about firewall rules appears, so click OK again.
- Press F5 in Server Manager. It should now say “Enabled”.
That’s a minute, probably less.
Server Manager often doesn’t refresh the status right away. “Disabled” can sit there for a solid 30 seconds after the switch.
Press F5, or close and reopen. The setting is applied, and only the interface lags.
SystemPropertiesRemotein the Run box jumps straight to the Remote tab. On a VM with 2 GB of RAM, Server Manager can take 20 seconds or more just to load. We’d skip all of that.
Enable RDP on Windows Server with PowerShell
PowerShell is faster than clicking around. On Server Core, it’s one of the two real options.
Open PowerShell as administrator and run these three lines. No restart is needed.
Set-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server' -Name "fDenyTSConnections" -Value 0
Enable-NetFirewallRule -DisplayGroup "Remote Desktop"
Set-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server\WinStations\RDP-Tcp' -Name "UserAuthentication" -Value 1| Line | What it does |
|---|---|
| The first | Flips the registry bit: fDenyTSConnections goes to 0 |
| The second | Opens the firewall, which still blocks 3389 otherwise |
| The third | Sets UserAuthentication to 1 to require NLA |
Most people get tripped up at the second line. The registry bit alone leaves the firewall closed.
A sanity check afterwards:
Get-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server' -Name "fDenyTSConnections"A value of 0 shows it worked. If it’s back at 1 after a policy refresh, a GPO is overriding you.
The fix for that is in the troubleshooting section.
All-in-one script
Drop this into Notepad and save it as enable-rdp.ps1. From an admin session, right-click it and choose “Run with PowerShell”.
# Windows Server Enable RDP: complete setup
# Run as Administrator
# 1. Enable Remote Desktop in registry
Set-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server' -Name "fDenyTSConnections" -Value 0
# 2. Force NLA on
Set-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server\WinStations\RDP-Tcp' -Name "UserAuthentication" -Value 1
# 3. Open the firewall
Enable-NetFirewallRule -DisplayGroup "Remote Desktop"
# 4. Make sure the service is actually running
Set-Service -Name TermService -StartupType Automatic
Start-Service -Name TermService
# 5. Confirm everything worked
Write-Host "RDP Status:" (Get-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server' -Name "fDenyTSConnections").fDenyTSConnections
Write-Host "NLA Status:" (Get-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server\WinStations\RDP-Tcp' -Name "UserAuthentication").UserAuthentication
Write-Host "Service Status:" (Get-Service TermService).Status
| Output line | Expected value |
|---|---|
| RDP Status | 0 |
| NLA Status | 1 |
| Service Status | Running |
If TermService shows Stopped, RDP won’t work even after enabling it. More on that under troubleshooting.
We’d keep these commands in a .ps1 file on a USB stick. It pays off for anyone doing four or five server setups a week.
If the execution policy blocks the script, run it once with this line from an elevated prompt. That beats changing the policy for the whole machine.
powershell.exe -ExecutionPolicy Bypass -File .\enable-rdp.ps1Enable RDP on Windows Server from CMD
Some people just prefer CMD, and that’s fair. On a fresh Server Core install, the first PowerShell launch can sit there compiling .NET assemblies.
CMD starts instantly. Both main lines need an elevated Command Prompt, and they apply at once with no restart.
reg add "HKLM\SYSTEM\CurrentControlSet\Control\Terminal Server" /v fDenyTSConnections /t REG_DWORD /d 0 /f
netsh advfirewall firewall set rule group="remote desktop" new enable=Yes
reg add "HKLM\SYSTEM\CurrentControlSet\Control\Terminal Server\WinStations\RDP-Tcp" /v UserAuthentication /t REG_DWORD /d 1 /f| Line | What it does |
|---|---|
| The first | Sets fDenyTSConnections to 0 under the Terminal Server key |
| The second | Opens the firewall |
| The third, optional | Turns NLA on |
On a typical server the second line reports three updated rules.
Those are the inbound Remote Desktop rules for TCP, UDP and shadowing, switched on together.
Server Core without a GUI
There’s no desktop, no Start menu and no Server Manager. There’s just a blinking cursor.
SConfig is the text menu that fills the gap.
- Type
SConfigand press Enter. - Pick 7 for Remote Desktop.
- Press E to switch it on.
- Choose 1, the more secure option that requires NLA, and confirm.
Then check the firewall separately. On some builds the “Remote Desktop” rule group stays disabled, and connections time out.
A typical case on a 2019 Core machine: SConfig sets the registry value and leaves the firewall alone, and 20 minutes go on finding it.
Ping works, and a telnet to 3389 is refused. The firewall rules are still disabled.
So after SConfig, exit to the command line with option 15 on current versions. Then run this:
netsh advfirewall firewall set rule group="remote desktop" new enable=YesChecking the Windows Server firewall for RDP
However you turned RDP on, verify the firewall separately. Skipping it stings more often than you’d think.
Get-NetFirewallRule -DisplayGroup "Remote Desktop" | Format-Table Name, Enabled, Direction
Enable-NetFirewallRule -DisplayGroup "Remote Desktop"
The first line lists the rules, and every inbound one should show Enabled as True. The second line fixes a False.
The GUI route goes through Windows Defender Firewall with Advanced Security. Under Inbound Rules, find the Remote Desktop ones, right-click and choose Enable.
It isn’t complicated, just easy to skip.
One more point catches people out on site. Windows Firewall only covers the OS.
| Also check between you and the server |
|---|
| A hardware firewall, such as a Sophos box, a pfSense or a Cisco ASA |
| An AWS security group |
| An Azure NSG |
Port 3389 has to be open on each of them. Perfect Windows Firewall rules still end in “connection timed out” when something upstream blocks the port.
RDP access for other users
By default only members of the Administrators group can sign in over Remote Desktop. Others go into the local “Remote Desktop Users” group.
| Method | How |
|---|---|
| GUI | System Properties > Remote tab > Select Users > Add > type the user name > Check Names > OK |
| PowerShell | Add-LocalGroupMember -Group "Remote Desktop Users" -Member "DOMAIN\jsmith" |
| CMD | net localgroup "Remote Desktop Users" /add "DOMAIN\jsmith" |
A domain controller has no local group. There you use the domain’s Remote Desktop Users group and the “Allow log on through Remote Desktop Services” user right.
We feel strongly about one thing: don’t share the built-in Administrator password between three people.
It seems fine until a DNS zone gets deleted at night. Event Viewer can’t tell you who did it, because everyone signed in as “Administrator”.
Separate accounts fix that. Our page on adding and creating users in Windows Server shows the setup.
Why NLA matters for Remote Desktop
Network Level Authentication, NLA for short, makes the client prove its identity before the server creates a session. It does that through CredSSP.
Without NLA, the server allocates memory, spins up a session and renders the sign-in screen for whoever connects. Credentials get checked only after that.
So any scanner that reaches port 3389 gets a full sign-in screen and server resources.
With NLA on, the check comes first. Fail it, and the server drops you at the network layer.
That blunts brute-force attempts and pre-authentication exploits.
Leave it on. We can’t think of a legitimate reason to turn it off in 2026, since every current client handles it.
Microsoft’s page on allowing access with Remote Desktop recommends keeping it too.
One line verifies it:
Get-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server\WinStations\RDP-Tcp' -Name "UserAuthentication"A 1 shows NLA is active. A 0 calls for a fix.
Securing the server afterwards
You wanted to turn RDP on and get back to your real task. We get it.
But five minutes on any sysadmin forum turns up someone who got hit through RDP this week. Exposed Remote Desktop is one of the most common ransomware entry points.
Attackers typically find an open 3389 within hours.
| Measure | What to do |
|---|---|
| Keep 3389 off the public internet | A VPN, or a list of trusted IPs in the firewall scope |
| Keep NLA on | See the section above |
| Strong passwords and lockout | Group Policy, under Account Policies |
| Audit logon events | Advanced Audit Policy, under Logon/Logoff |
| Move the port, optional | A random high port cuts scanner noise |
Swapping the port number
Bots scan 3389 day and night. A random high port cuts the noise, but it isn’t real protection by itself.
The value is PortNumber under the RDP-Tcp key shown below. The firewall rule needs the same port too.
HKLM\System\CurrentControlSet\Control\Terminal Server\WinStations\RDP-TcpOur separate walkthrough on changing the RDP port has all the details.
Known source IPs only
Open the Remote Desktop inbound rule in Windows Defender Firewall and go to the Scope tab. Add your office IP or VPN subnet under “Remote IP addresses”.
Now only those addresses can even try to connect.
A VPN
Or use a VPN and keep RDP off the internet entirely. WireGuard or OpenVPN will do, and so will an IPsec tunnel.
You connect to the VPN first and then use RDP over the internal network. We’d do this on every production machine.
Zero RDP ports face the internet.
Password complexity and lockout
| Policy | Where | Value |
|---|---|---|
| Password Policy | Computer Configuration > Windows Settings > Security Settings > Account Policies > Password Policy | A minimum length of at least 12, with complexity on |
| Account Lockout Policy | The same Account Policies node | A threshold. 5 bad attempts is a common choice |
Check the values in secpol.msc on your build, and don’t trust defaults. A shocking number of servers in the wild run with no lockout. Our password policy guide for Windows Server 2019 covers the settings.
Logon auditing
Turn on logon auditing in the same GPO area, for success and failure.
| Path |
|---|
| Computer Configuration > Windows Settings > Security Settings > Advanced Audit Policy Configuration > Audit Policies > Logon/Logoff |
Check the Security log after a week. Even servers on a private network often collect a surprising pile of failed logons.
Once auditing is on, these Event IDs matter for RDP monitoring.
| Event ID | Log | What it records |
|---|---|---|
| 4624 | Security | Successful logon. Filter for Logon Type 10 (RemoteInteractive) to see only RDP |
| 4625 | Security | Failed logon. Watch for repeated attempts from the same IP |
| 1149 | TerminalServices-RemoteConnectionManager/Operational | RDP network connection authenticated (user and source IP included) |
| 21 | TerminalServices-LocalSessionManager/Operational | Session logon succeeded |
| 24 | TerminalServices-LocalSessionManager/Operational | Session disconnected |
| 25 | TerminalServices-LocalSessionManager/Operational | Session reconnected |
This PowerShell line lists successful RDP logons in the last 24 hours:
Get-WinEvent -FilterHashtable @{LogName='Security';ID=4624;StartTime=(Get-Date).AddDays(-1)} | Where-Object {$_.Properties[8].Value -eq 10} | Format-Table TimeCreated, @{N='User';E={$_.Properties[5].Value}}, @{N='SourceIP';E={$_.Properties[18].Value}}Swap 4624 for 4625 to see failed attempts. More than a handful from unknown IPs shows that scanners are hammering your RDP port.
Enable RDP through Windows Admin Center
Almost everyone skips this method. Windows Admin Center is free and browser-based, and it toggles RDP with no RDP session to the machine.
It’s handy where WAC already runs on a jump box.
- Install WAC from Microsoft on your workstation or a management server, and open it in the browser.
- Add the target server with Add, then Servers, and enter its name or IP.
- Click the server name in the list.
- Scroll the left panel to Settings.
- Click Remote Desktop.
- Turn on “Allow remote connections to this computer”.
- Keep Network Level Authentication required.
- Save.
WAC talks to the server over WinRM, on ports 5985 and 5986. Those are often open when 3389 isn’t.
The catch: WAC has to sit on a machine you already trust, and the target needs PowerShell Remoting on.
For flipping RDP on a single machine, it’s overkill.
Group Policy for many servers
Clicking through Server Manager on 30 machines one by one isn’t an option. A GPO does it for the whole OU.
- Run
gpmc.mscto open Group Policy Management. - Create a GPO, or edit an existing one, and link it to your servers OU.
- Go to the Connections path in the table below.
- Set “Allow users to connect remotely by using Remote Desktop Services” to Enabled.
- In the Security folder next to it, enable “Require user authentication for remote connections by using Network Level Authentication”.
- Under the firewall path in the table, enable “Allow inbound Remote Desktop exceptions”.
- Run the update line on each target, or wait for the background refresh.
| Item | Path or value |
|---|---|
| Connections path | Computer Configuration > Policies > Administrative Templates > Windows Components > Remote Desktop Services > Remote Desktop Session Host > Connections |
| Firewall path | Computer Configuration > Policies > Administrative Templates > Network > Network Connections > Windows Defender Firewall > Domain Profile |
| Update line | gpupdate /force |
| Background refresh | 90 minutes plus a random offset |
Servers apply the GPO at the next policy refresh. The result is clean, consistent and repeatable.
A typical inherited environment: 12 of 25 servers have NLA on. The other 13 have it off, and nobody knows why.
There’s no documentation. One GPO and ten minutes later, all 25 match.
Turning it on remotely when Remote Desktop is off
RDP is off, and RDP was your plan for getting in. That’s annoying, but there are other routes.
All of them need network access and administrator credentials.
| Route | Port | How it works |
|---|---|---|
| PowerShell Remoting over WinRM | 5985 | On domain-joined servers, WinRM is enabled by default since Server 2012. Open a remote shell and run the Set-ItemProperty and firewall commands from there |
| PsExec from Sysinternals | 445 (SMB) | Runs the reg add line on the target. SMB is open on most domain networks |
| Remote Registry | The service’s own | Start the Remote Registry service on the target, connect from your workstation with regedit (File > Connect Network Registry) and set fDenyTSConnections to 0. The firewall still needs opening afterwards |
Enter-PSSession -ComputerName SERVER01
Invoke-Command -ComputerName SERVER01 -ScriptBlock { ... }
PsExec.exe \SERVER01 reg add "HKLM\SYSTEM\CurrentControlSet\Control\Terminal Server" /v fDenyTSConnections /t REG_DWORD /d 0 /f
sc \SERVER01 start RemoteRegistry| Line | Use |
|---|---|
| The first | Opens a remote shell |
| The second | Runs the same commands in one go, with them inside the braces |
| The third | Sets the registry value through PsExec |
| The fourth | Starts the Remote Registry service |
If none of those ports is open either, only out-of-band management or a physical visit is left.
Pack a laptop, and buy the NOC staff a coffee.
When you can’t connect
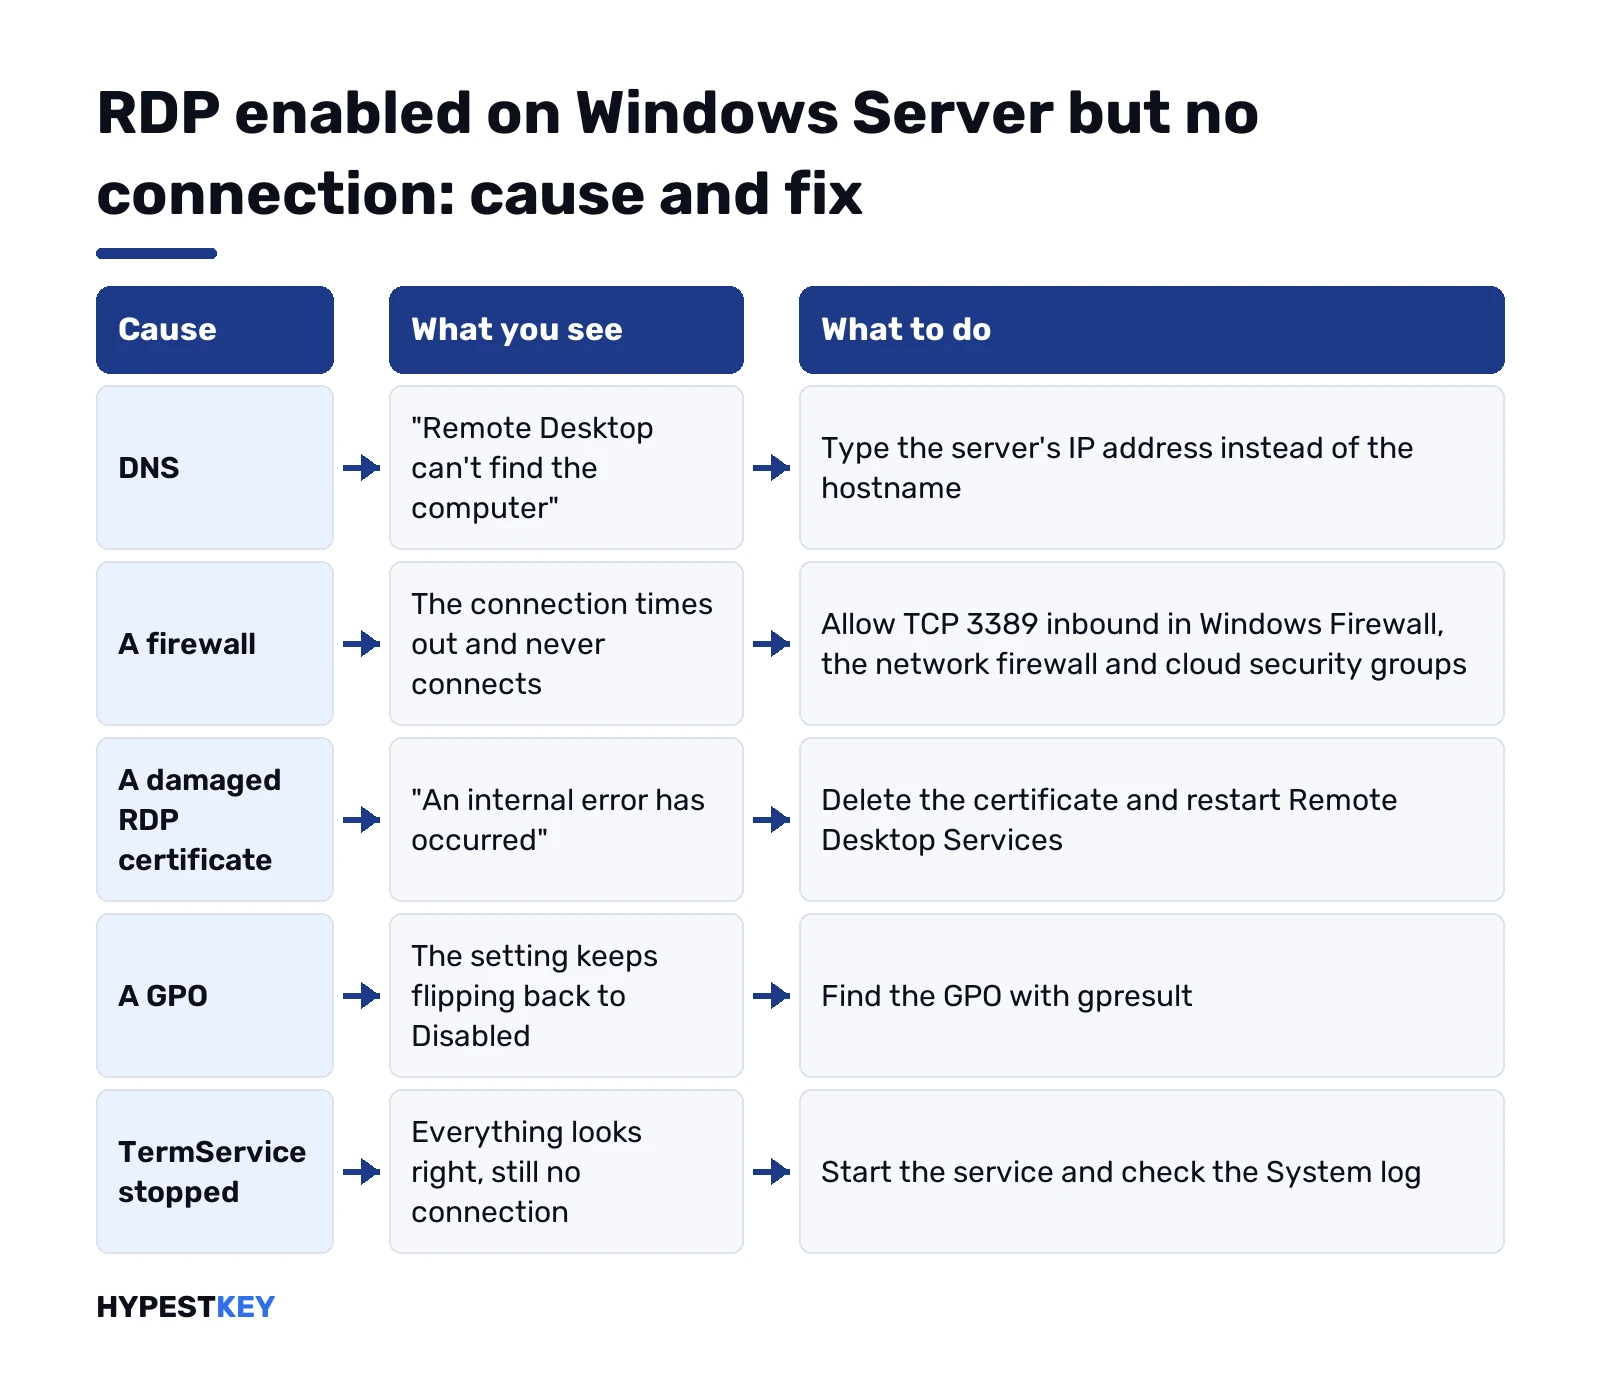
Check the usual causes in this order. Each can cost an hour, and some closer to three.
| Symptom | Usual cause | Fix |
|---|---|---|
| “Remote Desktop can’t find the computer” | DNS, nine times out of ten | Type the IP address instead of the hostname. ipconfig on the server console shows the right one |
| Times out, never connects | A firewall, almost always | Check Windows Firewall, the network firewall and cloud security groups for TCP 3389 inbound, or your custom port |
| “The remote computer requires Network Level Authentication” | Wrong credentials, clock skew or a domain trust problem on the server side | Check the DOMAIN\username format, or use .\username for local accounts. Kerberos tolerates about 5 minutes of clock skew |
| Server Manager shows “Disabled” after the switch | A slow refresh; it can lag for almost a minute on overloaded machines | F5, or close and reopen. The setting already applied |
| “An internal error has occurred” | A damaged self-signed RDP certificate | Delete the certificate and restart Remote Desktop Services |
| Keeps flipping back to Disabled | A GPO overwrites the local setting | Find the GPO with gpresult |
| Everything looks right, still no connection | The Remote Desktop Services service (TermService) is stopped | Start it, and check the System log |
This line from your workstation tells you in seconds if the port answers:
Test-NetConnection SERVER01 -Port 3389The internal error
This one shows up on 2022 machines, and it can eat far too much time. The self-signed certificate RDP uses has gone bad.
- Open
certlm.msc. - Go to Remote Desktop, then Certificates.
- Delete the server’s RDP certificate.
- Restart Remote Desktop Services. Windows generates a fresh certificate.
Also run qwinsta to confirm the RDP-Tcp listener shows up.
The setting that flips back
A GPO is overwriting your local setting. These two lines show which one:
gpresult /r
gpresult /h report.html
Look for “Allow users to connect remotely by using Remote Desktop Services” in the Remote Desktop Session Host policies. The GPO that sets it to Disabled wins at every refresh.
The stopped service
It sounds dumb, but the service can be stopped on servers with RDP “enabled” in the registry.
Get-Service TermService
Start-Service TermService
The first line should say Running. The second one starts the service.
If it won’t start or keeps stopping, check the System log for TermService errors. Usually it’s a certificate issue or a broken listener binding.
Disabling RDP on Windows Server again
A server is being decommissioned, or you’re going WinRM-only. In Server Manager, click “Enabled” next to Remote Desktop and choose “Don’t allow remote connections to this computer”.
PowerShell does it with two lines:
Set-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server' -Name "fDenyTSConnections" -Value 1
Disable-NetFirewallRule -DisplayGroup "Remote Desktop"
Don’t run them if RDP is your only way in. The session you’re in stays alive, but once you close it, that’s it.
It’s an easy mistake to make. The usual price: a four-hour round trip to a datacenter.
How many sessions at once
The system accepts two concurrent Remote Desktop sessions for administration. That needs no Remote Desktop Services role and no RDS CALs.
Those two sessions cover most small and mid-size setups: sign in, do your work, sign out.
| Need | What it takes |
|---|---|
| Three or more simultaneous users | The RD Session Host role, an RD license server and RDS CALs per user or per device |
| Users who work on the server and don’t administer it | The same three things |
RDS CALs come as a separate license from the base Windows Server CALs. Every user or device needs those base CALs to access the server.
Both are counted per user or per device. Our Windows Server CALs page lists the user and device CALs for each version.
RDS CALs must match the Session Host version or be newer. A Server 2025 host needs Windows Server 2025 RDS CALs, and we’d note that those also cover older hosts.
Connecting from your own machine
| Client system | How to connect |
|---|---|
| Windows | Win+R, mstsc, type the server’s IP or name, Connect |
| Mac | Install Windows App from the Mac App Store (free), add a PC and enter the IP. It is the successor of Microsoft Remote Desktop |
| Linux | xfreerdp /v:192.168.1.100 /u:Administrator in a terminal, or Remmina if you prefer clicking |
For a custom port, add it after a colon, as in 192.168.1.100:47293.
We’d always do one thing in mstsc before connecting. Click “Show Options”, open Local Resources and make sure the clipboard is shared.
For moving files, we’d map the local C: drive too. That’s quicker than SMB shares for a one-off transfer.
Our page on accessing Windows Server from a Mac covers the client settings for regular Mac use.
RDP differences between Windows Server versions
There are none in the steps. The Server Manager clicks, registry value, firewall group, PowerShell commands and Group Policy settings are identical.
| Version | Note |
|---|---|
| Windows Server 2025 | Same process as every version before it. Hotpatching, which installs many security updates without a restart, is available as a paid Azure Arc service. That helps on machines people reach over RDP all day |
| Windows Server 2022 | The first Windows Server with TLS 1.3 enabled by default at the operating system level. The steps have not changed at all |
| Windows Server 2019 and 2016 | Nothing different. Same clicks, same PowerShell commands, same registry keys, and Windows Admin Center manages both |
Need a key? Our Windows Server 2025 Standard key comes as a genuine license. Delivery is instant to email.
A server still on the 180-day evaluation needs one more step. Convert the evaluation to Standard before going to production.
Common mistakes when you enable RDP
- Setting the registry value and forgetting the firewall group.
- Trusting SConfig to open the firewall on Server Core.
- Exposing port 3389 straight to the internet.
- Turning NLA off to “fix” a connection problem.
- Editing a firewall rule with no second way in.
- Sharing the built-in Administrator account.
- Disabling Remote Desktop from inside the only RDP session.
- Fighting a local setting while a GPO keeps resetting it.
- Using the hostname when DNS is the problem.
- Counting on more than two sessions with no RDS CALs.
Related guides
Terms used on this page
| Term | Meaning |
|---|---|
| RDP | Remote Desktop Protocol, on TCP 3389 by default |
| NLA | Network Level Authentication, a credential check before the session starts |
| CredSSP | The protocol NLA uses to pass credentials |
| fDenyTSConnections | The registry value that turns Remote Desktop on with 0 and off with 1 |
| TermService | The Remote Desktop Services service |
| SConfig | The text menu for basic settings on Server Core |
| WinRM | Windows Remote Management, the transport behind PowerShell Remoting |
| PsExec | A Sysinternals tool that runs commands on another machine over SMB |
| GPO | Group Policy object, a set of settings applied to an OU |
| OU | Organizational unit, a container in Active Directory |
| Out-of-band management | Access that works apart from the operating system, such as iDRAC or iLO |
| Jump box | A trusted machine you manage other servers from |
| Firewall scope | The list of addresses a firewall rule accepts |
| RD Session Host | The role that lets many users work on the server at once |
| RDS CAL | The license each user or device needs for Remote Desktop Services |
Typical Remote Desktop problems on Windows Server
The colocation trip
A firewall rule goes wrong on a colocation server with no out-of-band access. The fix is two lines on site. The trip is 400 km.
The greyed-out toggle
One junior tech can’t flip the Remote Desktop setting. The account belongs to a regular domain user. With an admin account the toggle works.
The Core server
RDP is switched on through SConfig on a Core machine, and connections time out. The firewall group is still off. One netsh line opens it.
The ransomware weekend
An open 3389 port lets ransomware in. The file server is rebuilt from tape over a weekend. RDP now sits behind a VPN.
The mixed estate
Twelve of 25 servers have NLA on, and thirteen don’t. One GPO sets all 25 the same way.
The internal error
Some 2022 server answers with an internal error. Its RDP certificate is damaged. A fresh certificate fixes the connection.
Server versions and clients this guide covers
| Item | Details |
|---|---|
| Versions | Windows Server 2025, 2022, 2019 and 2016, Standard and Datacenter |
| Install types | Desktop Experience, and Server Core through SConfig |
| Essentials editions | Use the same Remote tab |
| Clients | mstsc on Windows 11, Windows App on macOS and FreeRDP on Linux, all with Network Level Authentication on |
FAQ
How do I enable RDP on Windows Server?
Open Server Manager, select Local Server and click Disabled next to Remote Desktop. Choose "Allow remote connections to this computer". We'd keep the Network Level Authentication box ticked and click OK. The firewall rules for port 3389 open by themselves.
Why is Remote Desktop disabled by default on Windows Server?
Port 3389 sits among the most scanned ports on the internet, and ransomware often comes in through it. So it stays off until an admin turns it on. We'd do that with NLA and a restricted firewall scope.
What PowerShell command enables Remote Desktop on Windows Server?
As administrator, set the fDenyTSConnections value under the Terminal Server key to 0 with Set-ItemProperty. Then we'd open the firewall with Enable-NetFirewallRule for the "Remote Desktop" display group. The full lines are in the PowerShell section above.
Can I enable RDP on Windows Server Core without a GUI?
Yes. Run SConfig, choose option 7, switch it on and pick the NLA option. Then we'd make sure the Remote Desktop firewall rules are on, with netsh or PowerShell.
How many users can connect to Windows Server over RDP at once?
Two concurrent sessions for administration, with no extra licensing. For more users, install the Remote Desktop Session Host role and set up an RD license server. We'd buy RDS CALs per user or per device to go with it.
What port does RDP use, and should I change it?
TCP 3389 by default. A random high port cuts bot noise. Real protection comes from a VPN or a firewall scope limited to trusted IPs, so we'd start there. The setting is the PortNumber value under the RDP-Tcp key in the registry.
What is Network Level Authentication, and should I keep it on?
NLA checks your credentials before the server creates a session. So scanners that haven't signed in never get a sign-in screen. We'd keep it on, since every current Remote Desktop client handles it.