Short answer: To connect to Windows Server, use Remote Desktop for the full desktop: run mstsc and enter the server name. A UNC path opens files, and PowerShell remoting or SSH handles commands. Over the internet we'd go through a VPN or Remote Desktop Gateway first, never an open port 3389.
The Windows Server you need to connect to sits in a rack, a cupboard or a datacenter. You sit somewhere else, usually with a laptop. There’s more than one way to connect to Windows Server from there, and the job decides which one fits.
A desktop, a folder, a command, a whole network. Each has its own tool.
- Remote Desktop, for the desktop.
- File shares and mapped drives, for a folder.
- PowerShell remoting or SSH, for a command.
- A VPN, for the whole network.
Small-business servers often get looked after from other buildings and other cities. Every method below has its place in a normal admin week. Each has a moment where it beats the others.
Each section shows how to switch a method on and how to use it. Locking it down and fixing failures come at the end.
| You want | Use |
|---|---|
| The full desktop | Remote Desktop, started with mstsc |
| Files and folders | A file share, opened by its UNC path |
| Commands and scripts | PowerShell remoting or SSH |
| Management without a session | Windows Admin Center or RSAT |
| Access from the internet | A VPN or Remote Desktop Gateway first, never an open RDP port |
The ways in, at a glance
| Method | Best for | Default port | Client you need |
|---|---|---|---|
| Remote Desktop (RDP) | Full desktop, GUI tools, installs | TCP/UDP 3389 | mstsc on Windows, Windows App on Mac, iOS and Android |
| File shares (SMB) | Copying and editing documents | TCP 445 | File Explorer |
| PowerShell remoting (WinRM) | Commands, scripts, many servers at once | TCP 5985 (HTTP), 5986 (HTTPS) | PowerShell |
| SSH (OpenSSH) | Cross-platform command line | TCP 22 | Any SSH client |
| Windows Admin Center | Browser-based management | HTTPS port chosen at setup | Modern browser |
| RSAT / Server Manager / MMC | Classic consoles from a workstation | RPC, WinRM | Windows 11 Pro or Enterprise with RSAT |
| VPN (RRAS or firewall VPN) | Reaching the whole network securely | IKEv2: UDP 500/4500; SSTP: TCP 443 | Built-in Windows VPN client |
The task decides. Moving files? A share. Configuring a role with a wizard? Remote Desktop. Checking disk space on twelve servers? One PowerShell line.
Third-party tools exist too. TeamViewer, AnyDesk, a VNC server. They can help when a firewall you don’t control blocks everything else. Each one is another agent to patch and another account to protect, though.
Picking by situation
| Situation | First choice | Why |
|---|---|---|
| A wizard or an installer with a GUI | Remote Desktop | It needs the desktop |
| One file from a share | File Explorer and the UNC path | No session needed |
| The same check on many servers | PowerShell remoting | One line reaches all of them |
| A weak mobile connection | PowerShell or SSH | Text needs little bandwidth |
| A mixed Windows and Linux team | SSH | Same tools and keys on both sides |
How to connect to Windows Server with Remote Desktop
- Find the server address. On the server,
ipconfigshows the IPv4 address. With working DNS, the host name is enough. - On your PC, press Win + R, type
mstscand press Enter. - Type the server name or IP into Computer. A custom port goes after a colon.
- Click Show Options if you want to save the connection or change the display size. The same place decides which local drives, printers and clipboard get shared.
- Click Connect and enter your credentials.
- On the first connection a certificate warning appears. Check that the name matches the server you meant, then confirm.
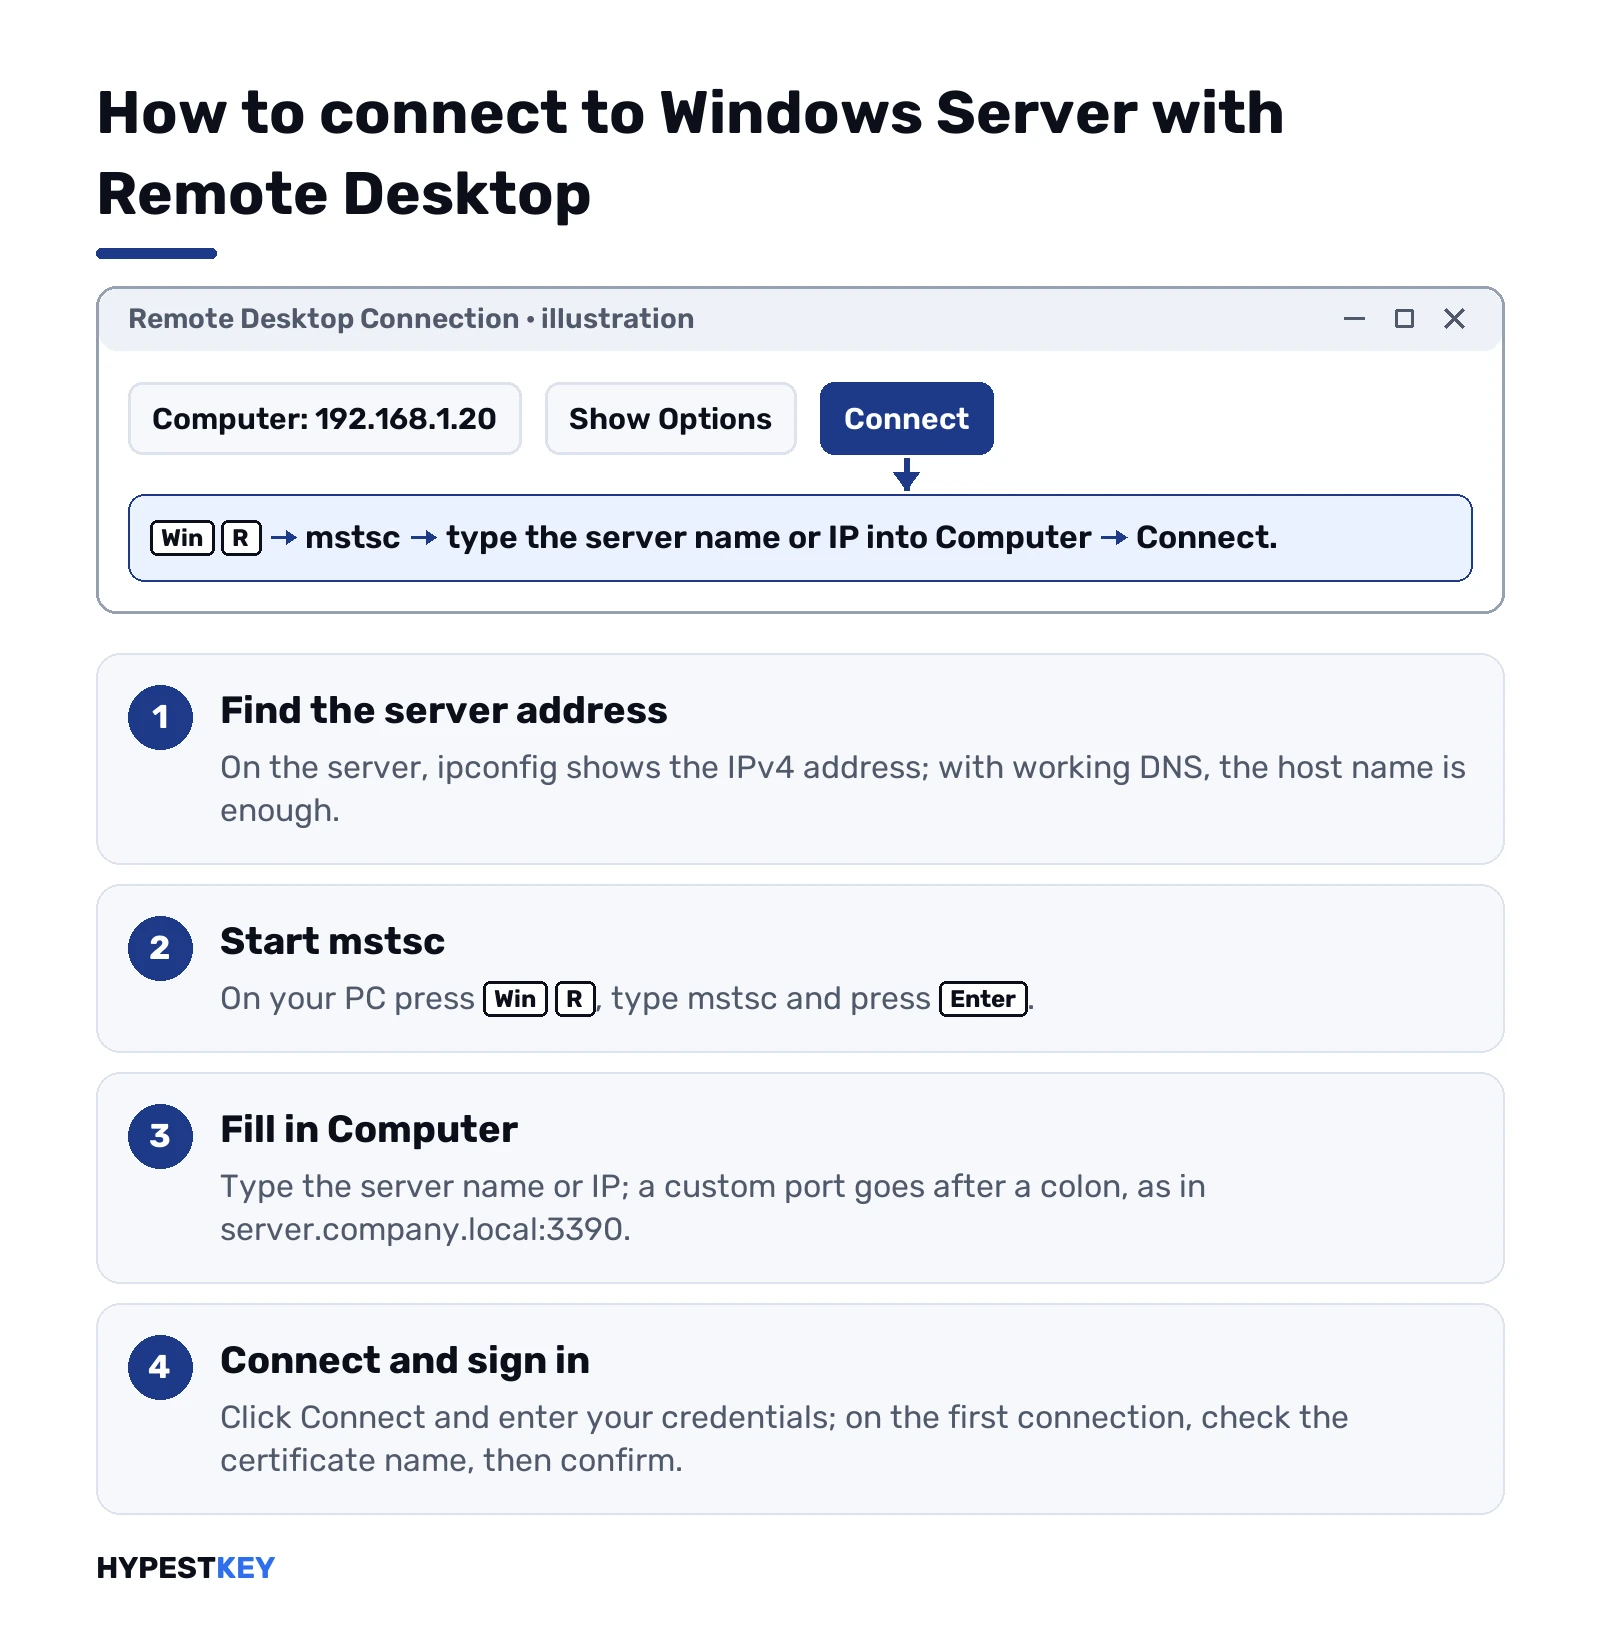
The server’s desktop opens in a window. The account needs remote access rights: an administrator, or a member of Remote Desktop Users.
The name of the tool comes from “Microsoft Terminal Services Client”. The formats for the address and the account look like this:
| Field | Example |
|---|---|
| Address by IP | 192.168.1.20 |
| Address with a custom port | server.company.local:3390 |
| Domain account | DOMAIN\username |
| Local account | SERVERNAME\username or .\username |
Save frequent connections as .rdp files from the General tab. We’d keep one per server. A second copy with the visual effects off is handy on weak hotel Wi-Fi.
On a Mac the client is Windows App from the App Store. It replaced Microsoft Remote Desktop. Our guide to accessing Windows Server from a Mac walks through it.
On an RDS host, the administrative session has its own switch. The old
/consoleswitch no longer does anything on current Windows versions.
mstsc /adminThe tabs behind Show Options
| Tab | What you set there |
|---|---|
| General | The address and user name; saving the connection as a file |
| Display | Window size and colour depth |
| Local Resources | Clipboard, printers and local drives inside the session |
| Experience | Visual effects, for slow links |
| Advanced | Certificate warnings and the Remote Desktop Gateway |
Most people never open these tabs. The Local Resources one is worth a look, though. Sharing a local drive into the session is the quickest way to move one file.
Switching Remote Desktop on
It’s off on a fresh install. You need a way to the server that isn’t RDP to turn it on. Local sign-in, the hypervisor console, or iLO and iDRAC.
- Open Server Manager and select Local Server.
- Click the “Disabled” value next to Remote Desktop. System Properties opens on the Remote tab.
- Select the option that turns on remote connections to this computer.
- Leave the box for Network Level Authentication ticked.
- Click Select Users to add non-administrators. They become members of the local Remote Desktop Users group.
- Click OK.
Windows turns on the firewall rule for port 3389 by itself. We’d still look: in Windows Defender Firewall with Advanced Security, the inbound Remote Desktop rules should be enabled. User Mode, TCP-In and UDP-In.
Two other doors to the same dialog. On the 2022 and 2025 releases there’s Settings, System, Remote Desktop. And everywhere, this runs it directly: SystemPropertiesRemote.exe.
On Server Core, use sconfig and pick option 7.
PowerShell does the whole thing in two lines. They’re handy on fresh builds:
Set-ItemProperty -Path 'HKLM:\System\CurrentControlSet\Control\Terminal Server' -Name fDenyTSConnections -Value 0
Enable-NetFirewallRule -DisplayGroup "Remote Desktop"
Test from a second machine before you close the local session. Locking yourself out of a remote server is a long drive.
For more detail per version, see our guide to enabling RDP on Windows Server. Group Policy and Server Core are in there too.
How many people fit into RDP at once
Two. Without Remote Desktop Services licensing, the system permits two simultaneous sessions, meant for administration only.
More users need the Remote Desktop Session Host role, and one RDS CAL per user or per device. Users who run applications on the server need the same. An unlicensed RDS host stops accepting connections when its grace period ends.
The message then: No Remote Desktop License Servers Available.
That two-session limit catches small offices out. A third admin signs in, and someone gets kicked off. Ask for one extra user, and the answer is RDS.
Two commands help here. qwinsta shows who’s signed in. rwinsta with a session ID resets a stuck session.
Disconnecting isn’t signing out
Disconnect, and your programs keep running in the session. Handy for a long install, bad for the session count. Sign out when you’re done.
Need licenses for more users? We sell the Windows Server 2025 RDS 50 User CAL, a genuine license, emailed instantly after payment. Match the CAL version to your RDS server version.
Files: shares and mapped drives
For documents you don’t need a desktop session. Open File Explorer on a computer in the same network and type the UNC path into the address bar. Two backslashes, the server name, one backslash, the share name:
\FILESERVER01\MarketingSign in when prompted. For daily use, map the share as a network drive, so it gets its own letter.
- On the server, share a folder. Right-click it, then Properties, Sharing, Advanced Sharing. Or use Server Manager, File and Storage Services, Shares.
- Set both the share permissions and the NTFS permissions.
- On the client, open File Explorer and enter the UNC path.
- To map it, right-click This PC and choose Map network drive. Pick a letter, enter the path and tick Reconnect at sign-in.
The same from the command line:
net use M: \FILESERVER01\Marketing /persistent:yesWhen a share refuses you
Most access problems are permissions. The effective permission is the stricter of the share setting and the NTFS setting. We’d call “Everyone: Full Control” on the share plus tight NTFS rules a sensible setup.
Wrong cached credentials are the other classic. Credential Manager holds saved passwords. And this clears mapped connections:
net use * /deleteSMB versions
SMB is the protocol underneath. Current server releases use SMB 3.x and disable SMB1. Very old clients and some NAS devices can’t get in until they’re updated.
Windows Server 2025 also requires SMB signing for outbound connections by default. That can break old storage that doesn’t sign.
Never publish SMB, port 445, to the internet. Remote staff should reach shares through a VPN. Or the files move to a cloud file service.
Connect to Windows Server with PowerShell remoting
For many admins, this is where most remote time goes. It uses a fraction of the bandwidth of RDP and works over a weak mobile connection. The tenth server gets exactly what the first one got.
Inside a domain, remoting is enabled by default on the server. It runs over WinRM on TCP 5985, or 5986 with HTTPS.
Enter-PSSession -ComputerName SERVER01 -Credential (Get-Credential)
Invoke-Command -ComputerName SRV01,SRV02,SRV03 -ScriptBlock { Get-Volume C }
Enable-PSRemoting -Force| Line | What it does |
|---|---|
| 1 | Opens an interactive session; the prompt changes to [SERVER01]: PS> |
| 2 | Runs one command on several servers at once |
| 3 | Switches remoting back on; run it in an elevated window on the server |
Type Exit-PSSession to leave an interactive session.
Outside a domain
On a workgroup server or a hosted VPS, Kerberos isn’t available. There are two ways round it. Use HTTPS with a certificate, on port 5986. Or add the server to the client’s TrustedHosts list:
Set-Item WSMan:\localhost\Client\TrustedHosts -Value "SERVER01"We’d prefer HTTPS. TrustedHosts turns a check off. It doesn’t add one.
PsExec, for older habits
Sysinternals PsExec still runs a remote command prompt:
psexec \SERVER01 cmdLeave the password off the command line, so it doesn’t end up in the history. PsExec prompts for it.
Connect to Windows Server over SSH
Windows Server 2019 and later support OpenSSH Server. So the usual SSH client works, from Windows, macOS, Linux or a phone.
| Release | State of OpenSSH Server | What to do |
|---|---|---|
| Windows Server 2025 | Installed, disabled | Server Manager, Local Server, set the OpenSSH entry to Enabled; or start the service |
| Windows Server 2019 and 2022 | Not installed | Add the Windows capability, then start the service |
Add-WindowsCapability -Online -Name OpenSSH.Server~~~~0.0.1.0
Start-Service sshd
Set-Service -Name sshd -StartupType Automatic
The first line is only for 2019 and 2022. Installing the capability creates a firewall rule named OpenSSH-Server-In-TCP for port 22. Check that it’s enabled.
Then sign in, with a local or a domain account:
ssh administrator@server01
ssh DOMAIN\user@server01
The default shell is Command Prompt. Many admins switch it to PowerShell with the DefaultShell value in the registry, under this key:
HKLM\SOFTWARE\OpenSSHKey-based authentication is worth the ten minutes it takes to set up. Microsoft’s OpenSSH for Windows Server guide covers both.
SSH shines in mixed environments. Linux admins can manage Windows boxes with the tools and key files they already use.
Management from a browser or a workstation
Two tools manage a server without any desktop session. Windows Admin Center in a browser, and the Remote Server Administration Tools on a Windows 11 workstation.
Windows Admin Center
Microsoft’s free gateway. Install it on a management server or on your workstation. Then open it at https://gatewayname, on the port you chose during setup.
Add servers by name and manage them from tiles. The list is long:
- Overview, events and services.
- Certificates and the firewall.
- Devices and storage.
- Files and the registry.
- Local users, roles and updates.
- A PowerShell console.
It covers most of the routine work we’d otherwise do over RDP. Use a proper certificate on the gateway. Self-signed ones trigger browser warnings and teach users to click through them.
Remote Server Administration Tools
RSAT installs the classic consoles locally. Server Manager, Active Directory, DNS, DHCP, Group Policy.
On Windows 11 Pro, Enterprise or Education it comes as optional features. Settings, System, Optional features, View features. Search for “RSAT” and add the tools you need. The Home edition can’t install RSAT.
Server Manager, MMC and Computer Management
- Server Manager. Manage, then Add Servers. Search Active Directory, or enter names or IPs. The dashboard then shows events, services and performance for all of them.
- MMC. Run
mmc.exeand add a snap-in such as Event Viewer. Choose “Another computer” and type the server name. - Computer Management. Right-click the top node and choose “Connect to another computer”. Event logs, shares, local users, services and disks, all remote.
Active Directory Users and Computers finds a domain controller by itself when your workstation is in the domain. Not in the domain yet? Our guide to joining Windows Server to a domain covers that part.
A small-business note. Windows Server 2016 Essentials still has the Remote Web Access portal, for shared folders and remote desktop links. Later versions dropped the Essentials Experience role.
VPN access: connect to a Windows Server network
A VPN puts your device on the server’s network first. RDP, SMB and PowerShell then travel inside the tunnel.
- Install the role. Server Manager, Manage, Add Roles and Features, Remote Access. Then the role service called DirectAccess and VPN, RAS for short.
- Start the wizard. Tools, Routing and Remote Access. Right-click the server and choose Configure and Enable Routing and Remote Access.
- Choose the configuration. Remote access by dial-up or VPN, for a server with one role. VPN access and NAT, when the server also routes traffic.
- Assign the adapters. Check which NIC faces the internet. A wrong assignment here exposes the internal side.
- Assign addresses. From your DHCP server, or from a static pool reserved for VPN clients.
- Set authentication. Windows authentication works. Certificates, or RADIUS with multi-factor authentication through NPS, are stronger.
- Open the firewall. The table below has the ports.
| VPN type | Needs |
|---|---|
| IKEv2 | UDP 500 and 4500, plus ESP when not behind NAT |
| SSTP | TCP 443 and a TLS certificate whose name matches the public address |
PPTP and L2TP
Avoid both. Microsoft has deprecated them in RRAS, and new RRAS installations on Windows Server 2025 don’t accept them by default. PPTP’s authentication can be cracked offline. L2TP without IPsec doesn’t encrypt anything.
On the client
Users go to Settings, Network & internet, VPN, Add VPN. They choose the built-in Windows provider and enter the server’s public name, the VPN type and their credentials.
The same client handles corporate VPNs and personal VPN services. For the latter, our review of the best free Windows VPN apps explains the difference.
In many small offices the VPN now lives on the firewall or the router, not on the server. That’s fine, and often simpler. The point stays the same: authenticate to the network first.
Remote Desktop Gateway, briefly
A gateway publishes RDP over HTTPS, on port 443. People outside sign in to the gateway. The gateway passes the session on to the server inside. Port 3389 never faces the internet.
It can enforce multi-factor authentication through NPS. In the Remote Desktop client, the gateway address goes under the Advanced tab, in the settings for connecting from anywhere.
For a handful of admins a VPN does the same job with less setup. For many users who only need their remote desktop, we’d look at the gateway.
Securing how you connect to Windows Server
Four layers. Nothing exposed directly to the internet. Strong authentication. Tight rules about who gets in, and from where. A patched and logged server.
Authentication
- Keep Network Level Authentication on. It checks credentials before a full session starts, and that blocks a lot of automated attacks.
- Add multi-factor authentication for every administrative path. Through Remote Desktop Gateway with NPS, your VPN, or a third-party MFA agent.
- Enforce strong passwords and an account lockout policy through Group Policy. Set the threshold high enough that a typo doesn’t lock out the only admin.
- Use separate admin accounts, not everyday user accounts with admin rights.
Access restrictions
- Scope firewall rules to the IP ranges that should get in. The VPN pool, or the office.
- Use a Remote Desktop Gateway, HTTPS on 443, or a hardened jump server. Not direct RDP from outside.
- Never accept direct remote desktop sessions to domain controllers from external networks.
- Moving RDP off 3389 cuts the scanning noise in the logs. Our guide to changing the RDP port in Windows Server shows how. We’d treat it as tidiness, not security.
Encryption and session settings
- Use TLS for RDP with a certificate from your CA. HTTPS for WinRM. A valid certificate for Windows Admin Center.
- Set idle-session limits in Group Policy, under Remote Desktop Session Host, Session Time Limits. 15 to 30 minutes usually balances safety and convenience.
- Limit drive and clipboard redirection on servers that hold sensitive data.
- Patch on a schedule. Missing updates remain the most common way in.
Monitoring
- Watch the Security log for event 4625, a failed logon. And for 4624 with logon type 10, a Remote Desktop logon.
- Alert on bursts of failures, and on sign-ins at unusual hours. Both often point to someone probing.
- Review who has remote access rights every quarter. People change roles. Group memberships don’t change by themselves.
When it won’t let you in
Work in order. Network first, then the service on the server, then the firewalls, then the account. Event Viewer on the server usually names the real cause.
Network and name resolution
Test the port, not just ping. Many servers block ICMP, so a failed ping proves little. Swap the port number for 445, 5985 or 22 as needed:
Test-NetConnection SERVER01 -Port 3389
Resolve-DnsName SERVER01
ipconfig /all- The IP works and the name doesn’t? It’s DNS, and the second line shows it.
- Over the internet, confirm that the public IP hasn’t changed. And that the router still forwards to the right internal address.
- Run the third line on both ends. It shows wrong gateways, wrong subnet masks and duplicate IPs.
Services
| Method | Service that must run | Quick check |
|---|---|---|
| RDP | TermService | Get-Service TermService |
| File shares | The Server service, LanmanServer | Get-Service LanmanServer |
| PowerShell remoting | WinRM | Test-WSMan SERVER01 from the client |
| SSH | sshd | The service, plus the OpenSSH-Server-In-TCP firewall rule |
Accounts and permissions
- Is the account locked, or the Windows Server password expired? Try a local sign-in to see whether it works at all.
- The RDP user must be an administrator or in Remote Desktop Users. And Group Policy mustn’t take away the right to log on through Remote Desktop Services.
- A message that the account isn’t allowed to sign in remotely points to that right.
- A “CredSSP encryption oracle remediation” error tells you the patch levels of client and server differ.
Performance and session limits
- “Too many users signed in”: the two administrative sessions are taken. Reset a stale one with
rwinsta. - A laggy session: lower the colour depth, and turn off wallpaper and animations on the Experience tab. Check CPU and memory on the server too.
- Intermittent drops: test at different times of day. That separates network congestion from server problems.
Last-resort options
- Use the hypervisor console or out-of-band management when every network path fails. iLO, iDRAC or IMM.
- Try another path. With RDP broken, PowerShell remoting or SSH can often restart the service.
- Restart Remote Desktop Services. It drops active sessions.
- Read the logs. System and Security in Event Viewer, plus the RDP-specific log named below.
Restart-Service TermService -ForceThe RDP log sits under Applications and Services Logs, Microsoft, Windows, TerminalServices-RemoteConnectionManager.
Rarely is the fault where it first looks. A methodical pass through these checks finds it faster than restarting things at random.
What to have ready before the first session
- The server’s name or IP address, and the port if it isn’t the default.
- An account with remote access rights, in the right format.
- The VPN details, when you’re outside the office.
- A second way in. A console, an out-of-band card, or a colleague on site.
- The name of the share, when it’s files you’re after.
The second way in is the one people skip. It only matters on the day the first way fails, and then it matters a lot.
A typical week: how admins connect to Windows Server
Monday, a role needs configuring through a wizard. That’s a Remote Desktop session. Tuesday, a colleague can’t find a spreadsheet, and the mapped drive answers it. Wednesday, twelve servers need a disk space check. One PowerShell line, and coffee.
Thursday is spent at a client’s office, so everything runs through the VPN. Friday the usual way breaks, and the hypervisor console saves the day. We’d set up every one of these before the day you need it.
Windows Server versions this guide covers
| System | What applies |
|---|---|
| Windows Server 2025, 2022 and 2019, Standard and Datacenter | Everything; Desktop Experience, and Server Core via sconfig and PowerShell |
| Windows Server 2016 | RDP, file shares and PowerShell; the SSH steps start with 2019 |
| Clients | Windows 11 24H2 and 25H2 with mstsc and RSAT, Windows App on macOS |
Which methods you settle on depends on your servers and your team. The order of priorities stays the same. Get in securely. Use the lightest tool that does the job. And know how to get back in when the usual way breaks.
Related guides
FAQ
How do I connect to Windows Server from my PC?
Press Win + R and type mstsc. Enter the server's name or IP address and click Connect. Sign in with an administrator account, or a member of the Remote Desktop Users group. Remote Desktop has to be enabled on the server first.
How do I enable Remote Desktop on Windows Server?
Open Server Manager and select Local Server. Click the value next to Remote Desktop and turn on remote connections to this computer. We'd keep Network Level Authentication on. On Server Core, run sconfig and pick option 7.
How many users can connect to Windows Server by RDP at the same time?
Two simultaneous sessions for administration, without extra licensing. More users need the Remote Desktop Session Host role and one RDS CAL per user or device.
Can I connect to Windows Server from a Mac?
Yes. Install Windows App from the Mac App Store, add the server as a PC and use RDP. For files there's Finder, Go, Connect to Server, with an smb address. For commands, SSH works once OpenSSH is enabled on the server.
Is it safe to open RDP port 3389 to the internet?
Nope. Exposed RDP ports get scanned and attacked constantly. Put a VPN, Remote Desktop Gateway or jump server in front. We'd also require multi-factor authentication and limit the firewall rules to known IP addresses.
Does Windows Server support SSH?
Yes, from Windows Server 2019 onward, through OpenSSH Server. On Windows Server 2025 it's installed by default and disabled. Enable it in Server Manager under Local Server, or start the sshd service.
Why does Remote Desktop say it can't connect to the remote computer?
Usually one of four things. Remote Desktop is turned off, or the firewall blocks port 3389. The name doesn't resolve, or the account lacks remote access rights. A port test with Test-NetConnection from your PC narrows it down.