Short answer: To change a Windows Server password for your own account, press Ctrl+Alt+Del, or Ctrl+Alt+End in Remote Desktop. Then choose "Change a password". Admins reset other users in Active Directory or Computer Management. We'd script it with Set-ADAccountPassword for more than a few accounts.
To change a Windows Server password, press Ctrl+Alt+Del, or Ctrl+Alt+End in Remote Desktop, and choose Change a password; admins reset other accounts in Active Directory Users and Computers, Computer Management or PowerShell. People rarely change a Windows Server password at a calm moment. An admin left without a handoff. A rotation deadline caught up with you. Or you suspect that someone else knows the password. The change itself takes seconds with the right tool.
To change a Windows Server password for your own account, three keys and one menu entry are enough.
Other people’s accounts go through Active Directory Users and Computers, Computer Management or one line of PowerShell. Service accounts need extra care. Every service that uses the account wants the new password too. This is the playbook we’d use on Windows Server.
| Account | Tool |
|---|---|
| Your own | Ctrl+Alt+Del, or Ctrl+Alt+End over RDP, then “Change a password” |
| Domain users | ADUC, ADAC or Set-ADAccountPassword |
| Local users | Computer Management, net user or Set-LocalUser |
| Service accounts | Update every service, task and app pool, or move to gMSA |
Keep a second admin account before you change a critical password.
Which account you’re changing
Windows Server has three kinds of accounts, and each changes differently.
- Local accounts live in the server’s own database. Computer Management or the net user command changes them.
- Domain accounts live in Active Directory and change through the AD tools.
- Service accounts run background services. The new password has to be entered wherever they’re used.
| Account type | Where it lives | Best tool to change it | Watch out for |
|---|---|---|---|
| Your own account (local or domain) | Server or Active Directory | Ctrl+Alt+Del / Ctrl+Alt+End | Policy rules on length, history, minimum age |
| Another local user | Server’s SAM database | Computer Management, net user, Set-LocalUser |
Reset loses access to the user’s EFS files and stored credentials |
| Another domain user | Active Directory | ADUC, ADAC, Set-ADAccountPassword |
Cached credentials, replication to other DCs |
| Service account | Local or Active Directory | Services console plus the account tool, or gMSA | Services fail to start after the change |
| DSRM (directory restore) account | Each domain controller | ntdsutil |
Separate per DC; not the domain admin password |
Your access matters as well. Sitting at the console with working admin credentials is the easy case. Managing remotely, or being locked out, leads down other paths. Those come further below.
Policy plays a part too. Domain rules on length, history and minimum age can block a change that looks perfectly reasonable. We explain the rules, and how to adjust them, in our guide to password policy in Windows Server 2019.
How to change your own Windows Server password
- Press Ctrl+Alt+Del at the console.
- In a Remote Desktop window, press Ctrl+Alt+End instead. The other combination goes to your own PC.
- Select Change a password.
- Check the account name. Edit it if it shows a local account by mistake.
- Type the old password, then the new one twice.
- Press Enter.
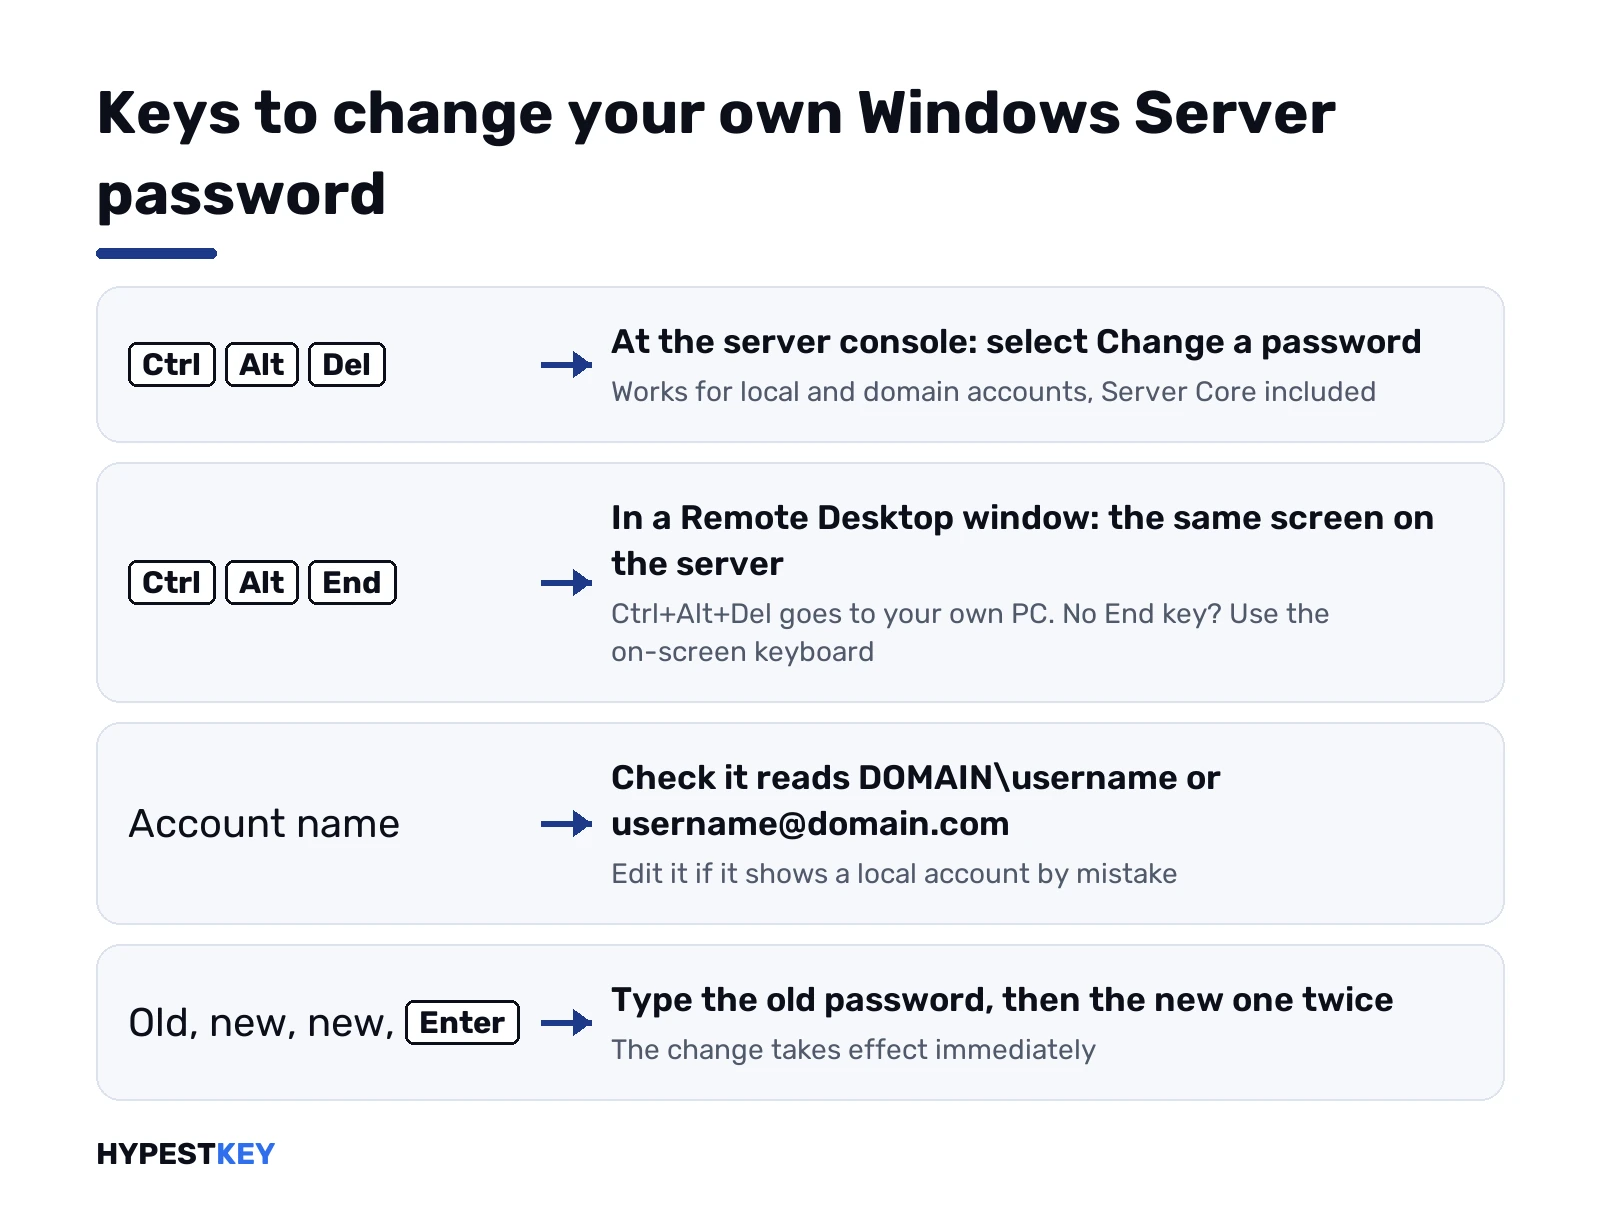
For a domain account the name should read in one of these two forms:
DOMAIN\username
username@domain.com
This works for local and domain accounts on every current release, Server Core included. The change takes effect immediately.
No End key on your keyboard? The on-screen keyboard in the session does the job.
Two other routes
On servers with the Desktop Experience, Settings works too. Accounts, Sign-in options, Password.
For local accounts an elevated command prompt is the quickest of all. This asks for the new password without showing it on screen:
net user %USERNAME% *About to change the password of the account you’re logged in with? Open a second session first, or confirm that a second admin account works. Then you still have a way back in.
Resetting another user’s Windows Server password
Getting someone back into an account takes a reset, not a change. The difference matters. A change needs the old password. A reset doesn’t. That’s why only admins or delegated helpdesk staff can do it, and why Windows warns about side effects.
Domain accounts in Active Directory
- Open Active Directory Users and Computers from Server Manager, under Tools. Or run
dsa.msc. - Find the user. In large domains, Action and then Find is faster than browsing.
- Right-click the account and choose Reset Password.
- Type the new password twice.
- Tick User must change password at next logon.
Two checkboxes in that dialog are worth knowing.
- User must change password at next logon. We’d tick it for any reset an admin starts. Only the user knows the final password then.
- Account Lockout Status. It clears a lockout from failed sign-in attempts in the same step.
Active Directory Administrative Center does the same from its Overview page, with a “Reset password” tile. It handles several domains in one console. You start it with dsac.exe.
While you’re in the account properties, look at the Account tab. “Password never expires” and the lockout status are both there.
Local accounts on a member or standalone server
- Right-click Start and open Computer Management.
- Go to Local Users and Groups, then Users.
- Right-click the account and choose Set Password.
Windows warns that a reset can cause irreversible loss of information for that user. EFS-encrypted files, personal certificates and saved passwords are at stake. With encrypted data in play, we’d let the user change it.
Domain controllers don’t have Local Users and Groups at all. On a DC every account lives in the domain.
New to account management on a server? Our guide to adding and creating users in Windows Server covers the basics.
After a reset: cached credentials
Domain users who are still signed in somewhere may keep failing to authenticate. Cached credentials are the reason. Ask them to sign out of every session, not just disconnect. Saved passwords for mapped drives and Outlook need updating too.
Change a Windows Server password with PowerShell and the command line
For local accounts there’s Set-LocalUser and the net user command. For domain accounts, Set-ADAccountPassword from the ActiveDirectory module, with its Reset switch.
Read the new password as a secure string. It never appears on screen or in your command history that way.
A local account, PowerShell 5.1 or later:
$Password = Read-Host "New password" -AsSecureString
Set-LocalUser -Name "Administrator" -Password $Password
A local account on the classic command line. It prompts for the password twice:
net user Administrator *A domain account, reset by an admin, with a forced change at next logon:
$Password = Read-Host "New password" -AsSecureString
Set-ADAccountPassword -Identity "jsmith" -Reset -NewPassword $Password
Set-ADUser -Identity "jsmith" -ChangePasswordAtLogon $true
Unlock-ADAccount -Identity "jsmith"
The last line clears a lockout, in case failed sign-ins had locked the account.
A bulk reset after a security incident
Every user in two departments at once:
$Departments = "Finance", "HR"
$NewPassword = Read-Host "Temporary password" -AsSecureString
foreach ($Dept in $Departments) {
    Get-ADUser -Filter "Department -eq '$Dept'" |
        Set-ADAccountPassword -NewPassword $NewPassword -Reset -PassThru |
        Set-ADUser -ChangePasswordAtLogon $true
}
It finds every user in the listed departments, resets the password and forces a new one at next sign-in. All in seconds. We’d hand out the temporary password through a separate channel, never with the user name.
A password status report for audits
Get-ADUser -Filter * -Properties PasswordLastSet, PasswordExpired, PasswordNeverExpires |
    Select-Object Name, PasswordLastSet, PasswordExpired, PasswordNeverExpires |
    Export-Csv -Path "C:\Reports\PasswordReport.csv" -NoTypeInformation
The CSV shows when each user last set a password. It flags expired passwords, and accounts set never to expire. That’s typically the first thing an auditor asks about.
Passwords on a remote server
Modern administration rarely happens at the physical machine. The options, from most to least hands-on:
- Remote Desktop. Closest to working at the console. Fine for one server, tedious for twenty. Our guide on connecting to Windows Server remotely has the options. RDP not on yet? Here’s how to enable RDP on Windows Server.
- Server Manager. Add the servers to All Servers. Right-click one and choose Computer Management, then Local Users and Groups. No separate RDP session needed.
- Windows Admin Center. Microsoft’s browser-based console, with a Local users and groups tool for each connected server.
- PowerShell remoting. Open a session on the server, then run the same Set-LocalUser lines as above.
Enter-PSSession -ComputerName SRV01For domain accounts, run the AD cmdlet from any machine with RSAT.
Remote tools let you rotate passwords in a night maintenance window, without a trip to the data center. They also let a mistake lock you out from far away. So the second-admin rule applies doubly.
A forgotten administrator password
Sign in with another administrator account and reset it. On a domain, another Domain Admin can reset it in Active Directory. With no admin access left, Microsoft offers no supported bypass. Restoring from a Windows Server backup, or reinstalling, is the clean way out then.
- Another admin account. The reason we always keep a second, documented admin account on standalone servers.
- A domain member server. A Domain Admin signs in and resets the local Administrator password with the net user command.
- Windows LAPS. Is the Local Administrator Password Solution managing the server? Then the current password can be read, given the right permissions.
- The Directory Services Restore Mode password. Reset it on a running DC with
ntdsutil. - Cloud VMs. Azure, AWS and others have console tools that reset the local admin password on a running VM. “Reset password” for an Azure VM, for example.
Windows LAPS is built into Windows Server 2019 with the April 2023 update, and into later versions. Reading the password looks like this:
Get-LapsADPassword -Identity SRV01 -AsPlainTextAnd the DSRM reset, typed line by line inside the tool:
ntdsutil
set dsrm password
reset password on server null
q
q
Third-party “password reset” boot disks exist. They’re unsupported, often blocked by BitLocker, and a bad idea on a domain controller. On a production server we’d rarely call them worth the risk.
Service accounts, without breaking services
Service accounts can’t be prompted at sign-in like a person. Change the password in Active Directory and forget one service, and it fails at its next start. Usually at 3 AM, after a reboot.
A SQL Server service account changed without preparation can take down a whole application stack.
- Find every service, scheduled task and IIS application pool that runs under the account.
- Change the password.
- Enter the new password in each of them.
- Restart the services.
Do it in a maintenance window. Better still, move the service to a group Managed Service Account.
Group Managed Service Accounts
With a gMSA, the domain controllers manage the password of a domain account. Member servers retrieve it automatically. Windows rotates it every 30 days by default.
According to Microsoft Learn’s gMSA guide, you need four things.
- Domain and forest functional level Windows Server 2012 or later.
- A Key Distribution Services root key in the domain, created once. Domain controllers can take up to 10 hours to use it.
- The gMSA itself.
- The account installed on each server. The service then logs on as the account, with an empty password field.
Add-KdsRootKey -EffectiveImmediately
New-ADServiceAccount -Name svc-app -DNSHostName svc-app.contoso.com -PrincipalsAllowedToRetrieveManagedPassword "AppServers"
Install-ADServiceAccount -Identity svc-app
The logon name for the service takes this form, dollar sign included:
CONTOSO\svc-app$Failover clusters themselves don’t support gMSAs. Services running on top of a cluster can use one.
Scripting the change for legacy service accounts
Older applications that don’t support gMSA need a coordinated change. This example resets the domain account and updates every local service that uses it:
$Account     = "CONTOSO\svc-legacy"
$NewPassword = Read-Host "New service password" -AsSecureString
Set-ADAccountPassword -Identity "svc-legacy" -Reset -NewPassword $NewPassword
$Plain = [System.Net.NetworkCredential]::new("", $NewPassword).Password
Get-CimInstance Win32_Service -Filter "StartName='CONTOSO\svc-legacy'" |
    ForEach-Object {
        $_ | Invoke-CimMethod -MethodName Change -Arguments @{ StartName = $Account; StartPassword = $Plain }
        Restart-Service -Name $_.Name
    }
Add -ComputerName to the CIM query to reach other servers. Add logging and error handling before you trust it in production.
Scheduled tasks need Set-ScheduledTask with the new credentials. IIS application pools need their identity updated in IIS Manager.
How often to rotate service accounts
It’s a balance. Each change carries some risk of an outage. So many organizations rotate service accounts quarterly or twice a year, not monthly. And at once when a compromise is suspected.
Before changing a critical password
Ten minutes of checks beat an evening of recovery.
- Backup access first. Few experiences match locking yourself out with no recovery path. Domains should have more than one admin. Standalone servers need a secondary admin account, kept for recovery.
- Usable passwords. A 64-character random string is secure, and painful during emergency maintenance at 3 AM. We’d keep long passwords in a password manager or a secured vault.
- Secure sharing. Never send credentials by plain email or text message. Use the vault, or a formal handoff with two people.
- Coordination. Tell application owners before you rotate an account their system depends on.
- Policy. Check that the new password meets the domain policy before the window starts.
- Documentation. Record when the password changed, who changed it and which systems were touched. Auditors ask. So does whoever troubleshoots next week.
Need a license for a new server? We sell a genuine Windows Server 2025 Standard key, and a Windows Server 2022 Standard key too. Delivery is instant to email.
When the server refuses the change
The usual reasons are policy rules.
- The new password is too short.
- It isn’t complex enough.
- It matches one of the remembered previous passwords.
- The minimum password age hasn’t passed since the last change. That’s one day in the default domain policy.
The generic “unable to update the password” error typically comes from one of these. This shows the rules that apply:
Get-ADDefaultDomainPasswordPolicyThe change went through, and sign-in still fails? Look at these causes next.
| Symptom | Cause | Fix |
|---|---|---|
| “Unable to update the password” | Length, complexity, history or minimum age rule | Check the policy with Get-ADDefaultDomainPasswordPolicy or any fine-grained policy that applies |
| Old password still works on some servers | Replication delay between domain controllers | Wait or force replication; password changes are sent to the PDC emulator right away, so sign-ins retry there |
| Account keeps locking after the change | Old password cached in a mapped drive, phone mail app or saved RDP connection | Clear entries with cmdkey /list and Credential Manager; update mobile devices |
| “The trust relationship between this workstation and the primary domain failed” | Computer account password out of sync | Run Test-ComputerSecureChannel -Repair -Credential (Get-Credential) before you think of rejoining |
| Password changed in AD but not in the cloud | Directory sync delay or error | Check the sync tool’s logs and start a sync cycle |
That trust error
Domain-joined computers change their own machine account password every 30 days by default. The error typically shows up after restores from old snapshots. The stored password no longer matches.
Repairing the secure channel in place often fixes it, without the downtime of a rejoin:
Test-ComputerSecureChannel -Repair -Credential (Get-Credential)For the cases where a rejoin is the only option, see our guide to joining Windows Server to a domain.
The built-in Administrator account is exempt from the account lockout threshold. That’s exactly why it needs a long, unique password. And why LAPS is worth setting up on member servers.
How often to change them
Change them at any sign of compromise, and when an admin leaves. Current NIST guidance advises against forced periodic changes for user passwords. Many organizations still rotate service and shared admin passwords on a fixed schedule.
What to tell the user afterwards
- The temporary password, through a channel other than email.
- That the next sign-in will ask for a new one.
- To sign out of every other session first.
- To update the phone, mapped drives and saved Remote Desktop connections.
Skip that last point, and the account locks again within the hour. It’s one of the most common follow-up problems after a reset.
Reset a Windows Server password using cmd: net user in detail
Plain Command Prompt, no modules, elevated. The asterisk version above is the safe one. A few more switches from Microsoft’s net user reference earn their place.
net user jsmith * /domain
net user jsmith /active:yes
net user jsmith /passwordchg:no
net user svc-backup /expires:never| Line | What it does |
|---|---|
| First | Resets a domain account from a member server; the operation runs on a domain controller of the primary domain |
| Second | Turns a disabled account back on |
| Third | Stops the user from changing the password, for kiosk or shared accounts |
| Fourth | Sets the account itself to never expire, which is a different thing from the password |
Limits worth knowing. User names can run to 20 characters, passwords to 127. And the password still has to clear the minimum length set by policy, so a short one gets refused here too.
Typing the password straight into the line works as well. We wouldn’t. It lands in the console history and on anyone’s screen behind you.
Forcing a LAPS rotation on the server
Suspect the local Administrator password leaked, on a server Windows LAPS manages? One line, run on that server itself:
Reset-LapsPasswordLAPS rotates the managed account at once, expired or not. Microsoft’s reference keeps it for rare cases like a breach and warns against frequent use.
The cmdlet prints nothing useful. The result sits in the Windows LAPS event log, and the new password is read with Get-LapsADPassword as shown earlier.
Windows Server versions these password steps cover
| System | Methods that apply |
|---|---|
| Windows Server 2016, 2019, 2022 and 2025 with the Desktop Experience | All methods |
| Server Core | The keyboard, net user and PowerShell methods |
| Active Directory steps | Domains at the Windows Server 2016 functional level or higher, with RSAT on Windows 11 |
- Windows Server 2022 Standard and Windows Server 2025 Standard, as domain controllers and member servers.
- Windows Server 2019 Standard with Windows LAPS after the April 2023 update.
- Windows PowerShell 5.1 with the ActiveDirectory module.
With the right tool for each account type, a password change stops being a stressful event. It becomes routine maintenance, and we’d say that’s what it should be.
Related guides
FAQ
How do I change my password on a Windows Server through Remote Desktop?
Press Ctrl+Alt+End inside the Remote Desktop window. Ctrl+Alt+Del gets caught by your own PC. Choose "Change a password", then enter the old password and the new one twice. No End key? The on-screen keyboard works too.
What is the command to change a password in Windows Server?
For a local account, the net user command with the account name and an asterisk, in an elevated prompt. It asks for the new password twice. For a domain account we'd use Set-ADAccountPassword from the ActiveDirectory PowerShell module.
Can I reset the administrator password on a domain controller?
Yes, with another Domain Admin account. Reset it in Active Directory Users and Computers, or with Set-ADAccountPassword. The Directory Services Restore Mode password is separate. That one is reset on each domain controller with ntdsutil.
Why does Windows Server say the password does not meet the requirements?
The new password breaks a policy rule. Too short, not complex enough, used recently, or changed again before the minimum password age. That age is one day by default in a domain. Get-ADDefaultDomainPasswordPolicy shows the rules that apply.
Will changing a service account password stop my services?
Yes, unless you update it everywhere the account is used. Every service, scheduled task and IIS application pool, followed by a restart. Group Managed Service Accounts avoid all that. Domain controllers rotate their passwords.
How often should Windows Server passwords be changed?
At any sign of compromise, and when an admin leaves. Current NIST guidance advises against forced periodic changes for user passwords. Many organizations still rotate service and shared admin passwords on a schedule.
can i reset the server password from cmd
Yes, from an elevated Command Prompt with admin rights. Run net user with the account name and an asterisk, and it asks for the new password twice. Add /domain on a member server to reset a domain account.
Is there a supported way to reset it with the installation disc?
Nope. Microsoft offers no supported password bypass from installation media. Another admin account, LAPS, a Domain Admin or a restore from backup are the clean routes. With none of those, it's a reinstall.