Short answer: To join Windows Server to a domain, set the server's DNS to your domain controllers. Confirm that it resolves the domain. Then run the Add-Computer cmdlet in PowerShell. System Properties and sconfig work too. After the restart, we'd sign in with a domain account.
To join Windows Server to a domain, set its DNS to a domain controller, then run Add-Computer in PowerShell or use Server Manager, and restart. A new member server, freshly installed, and a domain waiting for it: time to join Windows Server to the domain. The join itself takes a minute. The preparation decides whether that minute turns into an afternoon. Most failed joins trace back to DNS.
To join Windows Server to a domain, point the server’s DNS at a domain controller and confirm it can find the domain. Then run the join and restart.
- DNS on the domain controllers, never the router.
- Test the SRV lookup from the server itself.
- Join: System Properties, sconfig or Add-Computer.
- Restart, then check the secure channel and Group Policy.
There are three ways to run it: System Properties, sconfig on Server Core, or the Add-Computer cmdlet in PowerShell. We go through all of them, with the checks before and after.
| Point | What to know |
|---|---|
| DNS | Causes most failed joins: the server must use a domain controller (or AD-integrated DNS) as its DNS server, not the router or 8.8.8.8 |
| Fastest method | Add-Computer -DomainName contoso.com -Credential contoso\admin -Restart; the only one that scales |
| Right OU | -OUPath lands the computer account in the right OU, so Group Policy applies from the first boot |
| Join hardening | Since the updates that began in October 2022 (KB5020276), reusing an existing computer account can be blocked; delete the stale account or pre-stage it properly |
What you need before the join
Six points. Check them first, and the join itself rarely fails. That holds for every release from Windows Server 2016 to 2025.
| Prerequisite | How to check | Good result |
|---|---|---|
| Domain controller health | repadmin /replsummary and dcdiag on a DC |
No replication failures |
| DNS client setting | Get-DnsClientServerAddress |
Only DC / AD DNS addresses listed |
| Domain controller lookup | nltest /dsgetdc:contoso.com |
Returns a DC name and address |
| Time | w32tm /stripchart /computer:dc01.contoso.com /samples:3 |
Offset well under 5 minutes |
| Computer name | hostname |
Final name, unique in AD (15 characters or fewer) |
| Join permission | Your account’s group membership or OU delegation | Domain Admins, or delegated “Create Computer objects” |
Checking DNS
The new server must resolve the domain’s service records, the SRV records. That’s how Windows finds a domain controller.
Set the network adapter’s DNS to the IP of one or two domain controllers. Then query the records from the server itself.
Set-DnsClientServerAddress -InterfaceAlias 'Ethernet' -ServerAddresses 10.0.0.10,10.0.0.11
nslookup contoso.com
nslookup -type=SRV _ldap._tcp.dc._msdcs.contoso.com
The first lookup should return the IP addresses of the domain controllers. The second lists each controller with port 389.
If the lookup fails, stop. No join method works until DNS does.
Need a refresher on adapter settings? Our guide to configuring DNS servers shows the same dialog. It looks identical on Windows Server with the Desktop Experience.
Ports between the server and the domain controller
A join needs DNS, Kerberos, LDAP, SMB and RPC traffic to reach a domain controller. Inside one site the Windows Firewall profiles already permit this.
The ports matter mainly when something sits in between: a hardware firewall, a cloud security group or a VLAN filter.
| Service | Port |
|---|---|
| DNS | TCP/UDP 53 |
| Kerberos | TCP/UDP 88 |
| RPC endpoint mapper | TCP 135 |
| LDAP | TCP/UDP 389 |
| SMB (Netlogon, SYSVOL) | TCP 445 |
| Kerberos password change | TCP/UDP 464 |
| Global Catalog | TCP 3268 |
| RPC dynamic range | TCP 49152 to 65535 |
| Time (W32Time) | UDP 123 |
A quick test from the new server. Repeat it for ports 88 and 445.
Test-NetConnection dc01.contoso.com -Port 389How to join Windows Server to a domain with the GUI
This is for servers with the Desktop Experience. Server Manager gets you to the dialog in two clicks. The same dialog has worked since Windows Server 2008.
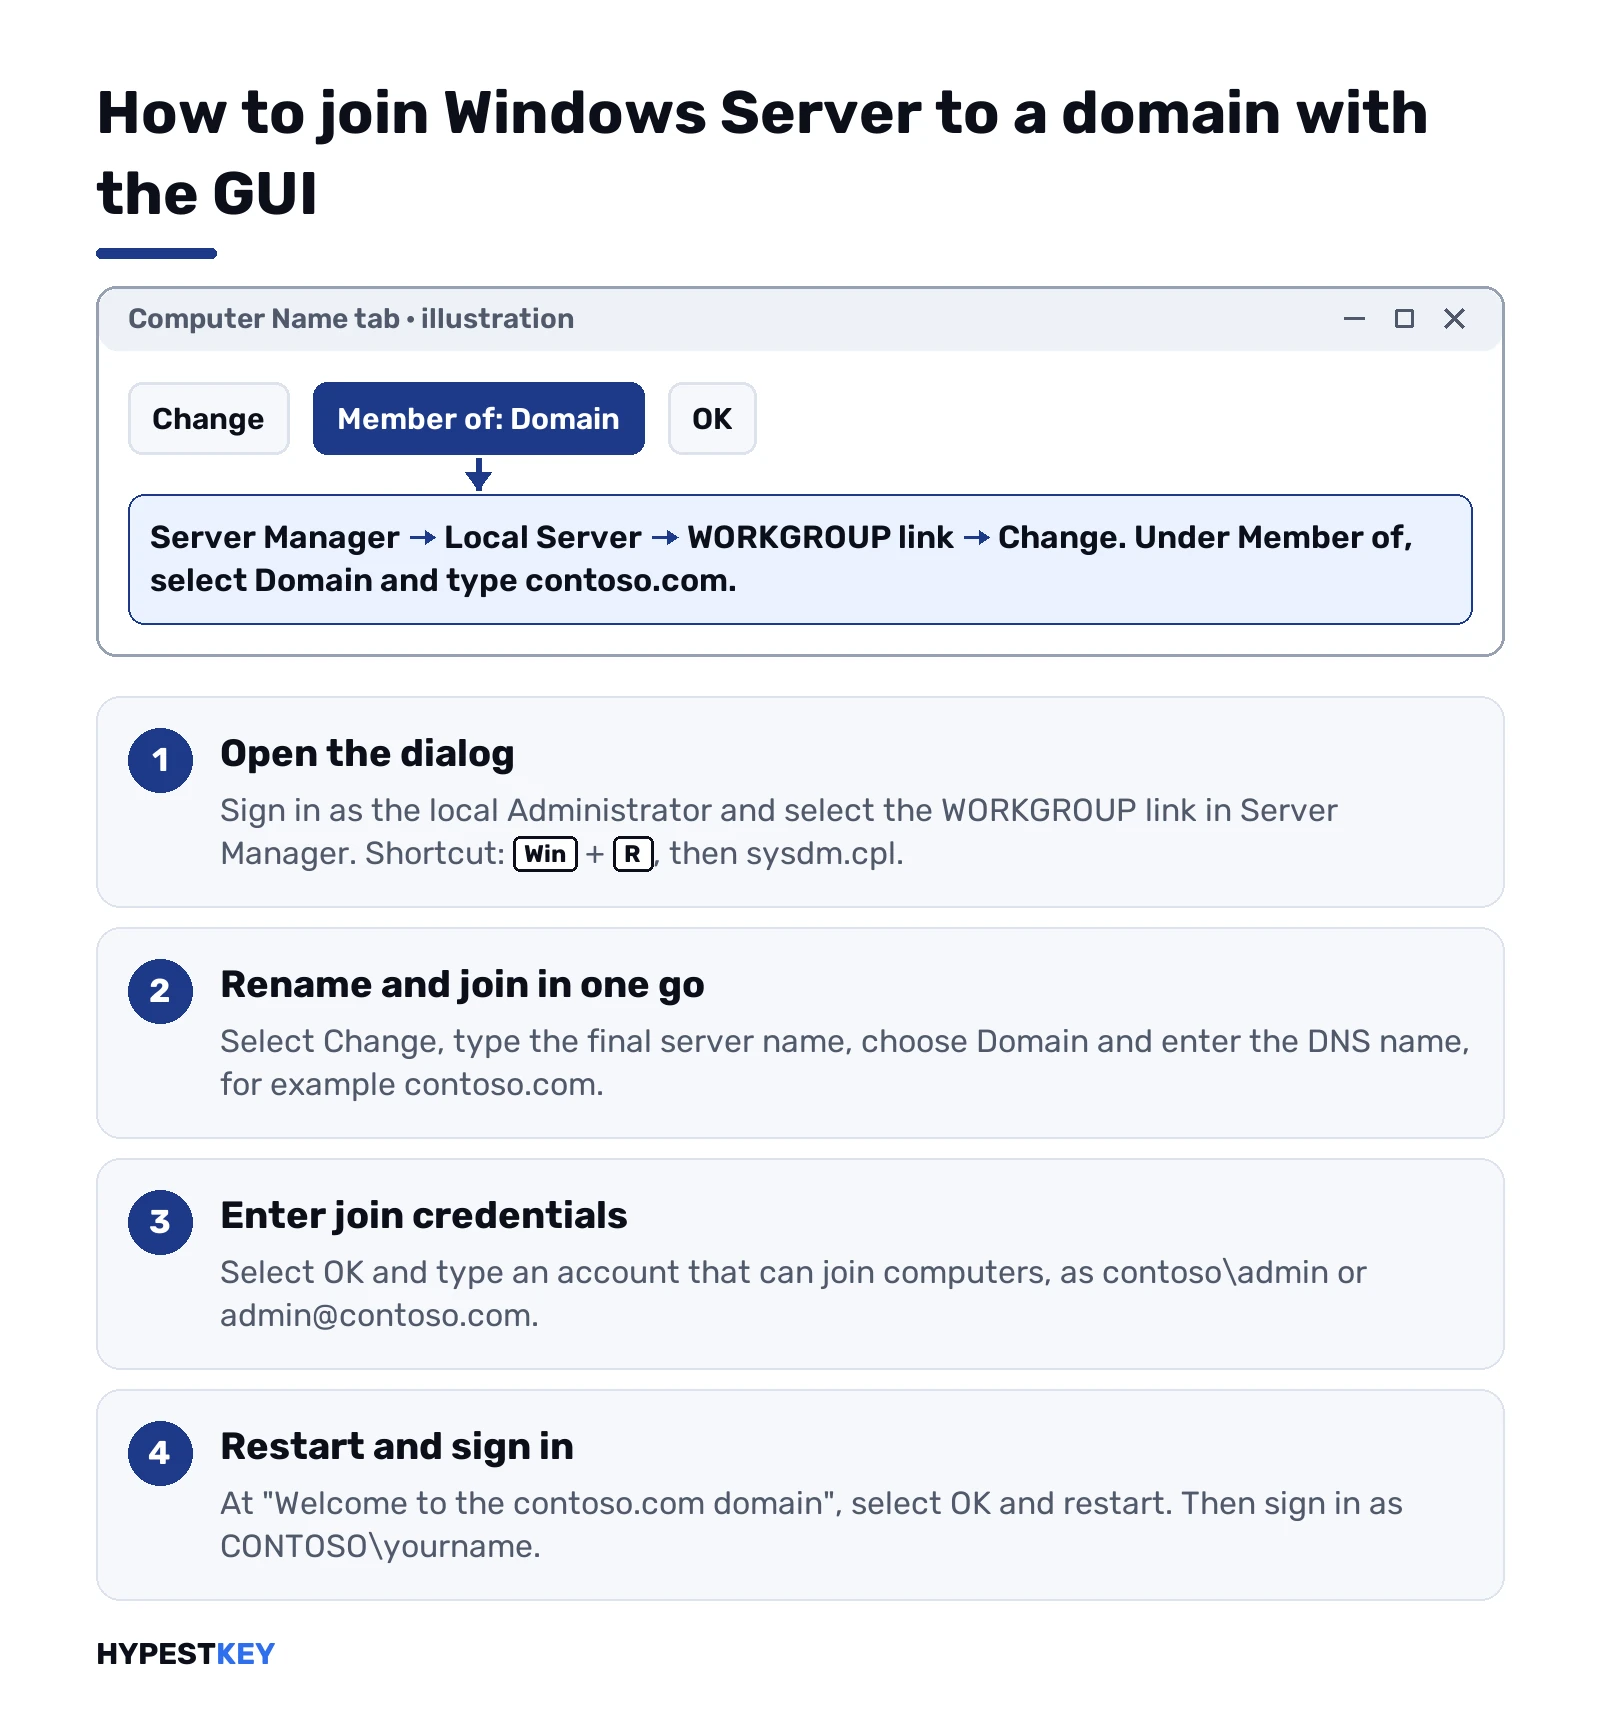
- Sign in with the local Administrator account. Forgot its password? Here’s how to change the Windows Server password.
- Open Server Manager, Local Server, and select the WORKGROUP link next to Workgroup.
- On the Computer Name tab, select Change.
- If the server still has its random setup name, type the final name now.
- Under Member of, select Domain and type the DNS name, for example contoso.com.
- Select OK. Enter the user name and password of an account that can join computers.
- When the “Welcome to the contoso.com domain” message appears, select OK and restart.
Notes on a few steps.
- Step 2. The shortcut: press Win+R and run
sysdm.cpl. - Step 4. Renaming and joining in one go saves a restart. It also avoids a second computer object.
- Step 5. The NetBIOS name, CONTOSO, also works. The full DNS name fails less often.
- Step 6. Use the form contoso\admin or admin@contoso.com.
After the restart, the sign-in screen offers Other user. Sign in as CONTOSO\yourname.
The computer account is created in the default Computers container. Unless it was pre-staged, or you redirect it. The OU section below covers that.
Joining Windows Server Core to a domain
Use the sconfig menu that opens at sign-in. It’s the GUI method in text form. On the 2022 and 2025 releases it’s available on Desktop Experience installations too.
- Sign in. If the menu doesn’t open by itself, type
sconfigand press Enter. - Set the DNS servers first, with option 8, Network settings. Use the addresses of the domain controllers.
- Choose option 1, Domain/workgroup. Then press D.
- Enter the domain name, then the user with join rights, then the password in the pop-up.
- Accept the offer to change the computer name if needed. Then restart.
As a rule, experienced admins skip sconfig. They use the PowerShell method directly in the Core console, and the result is identical.
Join Windows Server to a domain with PowerShell
Run Add-Computer from an elevated Windows PowerShell 5.1 window. That’s built into every current Windows Server release.
One line adds the server, optionally renames it, places it in an OU and restarts. It’s the method we’d use for every build, because it can be pasted into a runbook or a deployment script.
Add-Computer -DomainName contoso.com -Credential contoso\admin -Restart
Add-Computer -DomainName contoso.com -NewName SRV-FILE01 -OUPath "OU=Servers,OU=IT,DC=contoso,DC=com" -Credential contoso\admin -Restart
Add-Computer -DomainName contoso.com -Server dc02.contoso.com -Credential contoso\admin -PassThru -Verbose| Line | What it does |
|---|---|
| First | The basic join; it prompts for the password |
| Second | Joins, renames and places the account in a specific OU, in one go |
| Third | Targets a specific domain controller, for example in a branch site |
One detail about the third line. Since August 2024, Microsoft’s documentation states that the Server value must be the controller’s full DNS name. Short and NetBIOS forms are out. The join hardening changes are the reason.
The PassThru and Verbose parameters print the result. That helps in scripts.
To join a remote server that’s still in a workgroup, run the command from your admin machine. Add the ComputerName parameter and a LocalCredential for that server’s Administrator. The cmdlet doesn’t depend on PowerShell remoting for this.
netdom still works
The netdom tool still works on current versions. It ships with the AD DS management tools, though. So it’s present on domain controllers and on servers with RSAT installed. Not on a fresh member server.
Where it exists, it suits batch files and environments that restrict PowerShell.
netdom join %computername% /domain:contoso.com /userd:contoso\admin /passwordd:* /reboot:10
Install-WindowsFeature RSAT-ADDS-Tools
The asterisk after the password switch makes the tool prompt for the password. Nothing gets stored in the script. The second line adds the tool to a member server.
Where the computer account goes
By default a joined server lands in the Computers container. OU-linked Group Policy objects don’t apply there.
Two ways around that: pre-stage the account in a Servers OU, or pass the OU path during the join. Either puts the server under the right policies from its first boot. Join rights can then be delegated, too.
Pre-stage from a domain-joined admin machine, with the Active Directory module. Then join the server under that name.
New-ADComputer -Name SRV-FILE01 -Path "OU=Servers,OU=IT,DC=contoso,DC=com"By default, any authenticated user may create up to 10 computer accounts in the domain. The setting is called ms-DS-MachineAccountQuota.
Many organisations set that to 0 and grant the right through OU delegation. We’d call that the cleaner choice.
The join hardening, KB5020276
Security updates released from October 2022 onward make Windows refuse to reuse an existing computer account. There are three exceptions.
- The joining user created the account.
- The joining user belongs to Domain Admins, or to a similar group.
- The account owner is trusted by policy.
Rebuilt servers that keep their old name hit this most. The join fails with an error: an account with the same name exists, and reuse was blocked.
The fixes, in order of preference:
- Delete the old computer object before the rebuild.
- Join with a member of Domain Admins.
- Have the account re-created by the person who will join it.
Microsoft describes the rules, and the policy for trusted account owners, in KB5020276: Netjoin domain join hardening changes.
When the server can’t reach a domain controller
Use offline domain join, with the djoin tool. It suits isolated build networks and branch offices.
- On a domain-joined admin machine, create the computer account and a provisioning file. That’s the first line below.
- Copy the file to the new server.
- Apply it there with the second line, elevated. Then restart the server.
djoin /provision /domain contoso.com /machine SRV-BR01 /machineou "OU=Servers,DC=contoso,DC=com" /savefile C:\odj\SRV-BR01.txt
djoin /requestODJ /loadfile C:\odj\SRV-BR01.txt /windowspath %SystemRoot% /localos
On the next boot with a network path to a controller, the server is already a member.
Treat the file like a password. It contains the machine account secret.
Checks after the join
After the restart, confirm four things. The server belongs to the domain. Its secure channel works. Group Policy applied. And a domain user account can sign in.
(Get-CimInstance Win32_ComputerSystem).Domain
Test-ComputerSecureChannel -Verbose
gpupdate /force
gpresult /r /scope computer
Five minutes of checks now prevent strange authentication errors later. Then move on to the server’s real configuration.
- Local administrators. Add a domain group, for example CONTOSO\Server-Admins, to the local Administrators group. Ideally through Group Policy or LAPS, not by hand.
- Service accounts. Move services from local accounts to group managed service accounts, where the application supports it.
- Remote access. Check that Remote Desktop still works under the domain firewall profile. Our guide on enabling RDP on Windows Server covers the settings. Moving it off 3389? See changing the RDP port.
- Backups and monitoring. Add the server to both. It’s a good moment to schedule the first Windows Server Backup.
- Documentation. Record the name, the role, the OU and the join date in your asset list.
Why a join fails
In most cases it traces back to DNS. Then come time differences, duplicate or blocked computer accounts, missing permissions and blocked ports.
The error text usually points at the cause.
| Symptom or message | Likely cause | Fix |
|---|---|---|
| An Active Directory Domain Controller for the domain could not be contacted | Server uses public or router DNS; SRV records missing | Point DNS at the DCs; check with nslookup -type=SRV |
| Account with the same name exists; reuse blocked | Stale computer object, KB5020276 hardening | Delete the old object or join as a Domain Admin |
| Access is denied | No join permission or quota of 10 reached | Use a delegated account or pre-stage the computer |
| Kerberos or clock errors | Time differs more than 5 minutes from the DC | w32tm /config /syncfromflags:domhier /update after the join, or set the time manually before it |
| The specified server cannot perform the requested operation | Firewall between server and DC | Open the ports listed above |
| Trust relationship failed (later, after a snapshot restore) | Machine password out of sync | Test-ComputerSecureChannel -Repair -Credential contoso\admin |
Windows writes a detailed log of every join attempt. When the message on screen is vague, the last lines of that file typically name the exact failing step.
%windir%\debug\netsetup.logNever clone a domain-joined server without Sysprep. Two machines with the same SID and computer account fight over the secure channel. One of them keeps falling out of the domain.
Member or domain controller
They aren’t the same thing. A member uses Active Directory. A domain controller hosts it.
For a controller, you install the AD DS role and promote the server. The promotion replicates the directory and usually adds DNS. A member join is the normal first step.
Install-WindowsFeature AD-Domain-Services -IncludeManagementTools
Install-ADDSDomainController -DomainName contoso.com -InstallDns -Credential (Get-Credential contoso\admin)
Before promoting, plan the site placement, the Global Catalog role and backups of system state.
A new controller deserves more care than a file server. Every other machine in the site will depend on it.
Best practices for member servers
Good hygiene keeps a growing server estate manageable. None of it is complicated. Each habit pays off the first time you troubleshoot a policy or an authentication problem at 2 a.m.
- Create OUs by role, such as file, SQL or RDS. Group Policy can then target each type of server.
- Use a naming convention that shows role and location, for example LON-SQL02.
- Find stale accounts with the command below, and remove decommissioned servers.
- Define AD sites and subnets in multi-site networks. Servers then authenticate against a nearby controller.
Search-ADAccount -AccountInactive -ComputersOnly -TimeSpan 90.00:00:00For user accounts on the newly joined servers, see our guide to adding and creating users in Windows Server.
A short runbook for every new server
- Give the server its final name.
- Point DNS at the domain controllers and test the SRV lookup.
- Check the time against a controller.
- Pre-stage the account, or have the OU path ready.
- Run the join and restart.
- Check the domain name, the secure channel and Group Policy.
Join Windows Server to a domain without a domain admin on site
Branch office, local tech, no domain credentials to hand out. Microsoft’s Add-Computer reference has a pattern for exactly that.
First, on a domain-joined admin machine, create the account with a temporary join password.
New-ADComputer -Name SRV-BR02 -AccountPassword (Read-Host -AsSecureString "Temp join password")Then, on the new server, which already carries the name SRV-BR02:
$joinCred = New-Object pscredential -ArgumentList ([pscustomobject]@{ UserName = $null; Password = (Read-Host -AsSecureString "Temp join password")[0] })
Add-Computer -DomainName contoso.com -Options UnsecuredJoin,PasswordPass -Credential $joinCred -Restart
Note the empty user name. Microsoft’s reference says it has to be null with PasswordPass, because the password is the machine’s own.
After the join, Windows replaces that temporary password through the normal machine account routine. So it’s useless the next day.
Through a read-only domain controller
Only an RODC in that branch? Then the JoinReadOnly option.
The computer account has to exist already and sit in the allowed list of the password replication policy. And its password? Replicated to that RODC first, before anyone runs the join.
From one domain to another
Same cmdlet, one extra credential. UnjoinDomainCredential takes an account that may remove the server from the old domain, and Credential the one for the new domain.
Add-Computer -DomainName fabrikam.com -UnjoinDomainCredential contoso\admin -Credential fabrikam\admin -RestartGroup memberships and local profiles from the old domain don’t travel. We’d plan the new admin group before the move.
Repairing the trust instead of a rejoin
The error everybody knows: the trust relationship between this workstation and the primary domain failed.
Microsoft’s join guide names two causes. The machine password is out of sync, or the computer account was deleted or damaged. The PowerShell repair is in the error table above. No PowerShell at hand? Then netdom, signed in as the local administrator.
netdom verify SRV-FILE01 /domain:contoso.com
netdom resetpwd /server:dc01.contoso.com /userd:contoso\admin /passwordd:*
netdom reset SRV-FILE01 /domain:contoso.com
Restart afterwards. A deleted account is the one case where only a full rejoin helps. Workgroup, restart, then the domain again.
The steps are on Microsoft Learn under Join a computer to a domain, with tabs for Command Prompt and PowerShell.
Windows Server versions this domain join guide covers
The steps apply to the versions below, joining an Active Directory domain whose controllers run Windows Server 2016 or later. With current cumulative updates, the join hardening applies to all of them.
| Member server | GUI | sconfig | Add-Computer |
|---|---|---|---|
| Windows Server 2025 | Yes | Yes (Core and Desktop Experience) | Yes |
| Windows Server 2022 | Yes | Yes (Core and Desktop Experience) | Yes |
| Windows Server 2019 | Yes | Yes (Core) | Yes |
| Windows Server 2016 | Yes | Yes (Core) | Yes |
Building a new member server? Our Windows Server 2025 Standard key comes as a genuine license, and so does the Windows Server 2022 Standard key. Delivery is instant to email.
A domain join changes how a server works. Sign-in, policy and permissions now come from Active Directory. That simplifies administration and adds a dependency on the controllers.
Get DNS right and put the account in the right OU. The rest takes one line.
FAQ
What permissions do I need to join a server to a domain?
Members of Domain Admins can always join computers. Other users can join up to 10 computers by default, unless the quota was lowered. Admins can also delegate the right to create computer objects in a specific OU, and that's the route we'd take.
Why does the join say the domain controller could not be contacted?
Almost always DNS. The server is probably using the router or a public resolver. Point its DNS at the domain controllers. We'd test the SRV lookup for the domain before trying again.
Can I rename the server and join the domain at the same time?
Yes. In the GUI, change the name and the domain in the same dialog. In PowerShell, add the NewName parameter to the join command. One restart then covers both changes.
Do I have to restart after joining a domain?
Yes. The membership, Group Policy and domain sign-in only take effect after a restart. We'd add the Restart parameter to the join command, or restart when the welcome message appears.
How do I remove a server from a domain?
Use the Remove-Computer cmdlet, or choose Workgroup in System Properties. Make sure you know the local Administrator password first. Afterwards we'd delete the computer object in Active Directory.
How do I fix the trust relationship error on a member server?
Sign in with a local admin account and repair the secure channel with Test-ComputerSecureChannel. It resets the machine password. There's no need to leave and rejoin the domain, and we'd try this first.
Does joining a domain change my Windows Server license?
Nope. Domain membership has nothing to do with activation. A Standard or Datacenter key activates the same way before and after the join. Client access licenses are counted per user or device. Being in the domain doesn't change that.
Can someone without domain admin rights join the server?
Yes. Pre-create the computer account with a temporary password, then join with the UnsecuredJoin and PasswordPass options and an empty user name. Windows replaces that password after the join. A delegated "Create Computer objects" right on an OU works too.